News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities (opens Security Week in a new tab)
The flaws could lead to arbitrary code execution, authorization bypasses, and privilege escalation. The post Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities appeared first on SecurityWeek.
-
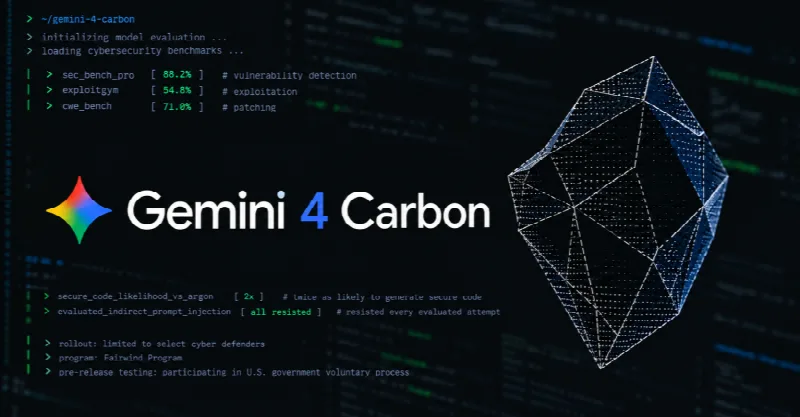
Google's Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching Vulnerabilities (opens The Hacker News in a new tab)
Google on Wednesday took the wraps off Gemini 4 Carbon, its latest frontier model with state-of-the-art cybersecurity and long-horizon capabilities. "It shows significant gains across coding and agentic tasks as well as across key capabilities critical for cybersecurity defense, landing a firm lead...
-
Volt Typhoon targeted enterprise control planes via ever-changing “Silent Train” relay network (opens Help Net Security in a new tab)
Volt Typhoon, a Chinese state-sponsored APT group that’s focused on cyberespionage and United States’ critical infrastructure, has been using a covert, constantly rotating relay network to hide its most sensitive intrusions, Lumen’s Black Lotus Labs revealed on Wednesday. This network, dubbed...
-
Petkit Automatic Cat Litter Box Sale (2026) (opens Wired in a new tab)
As WIRED’s resident pet tech tester, I have lots of opinions on what’s worth your money. Petkit’s automatic litter boxes are my top picks—and my favorite models are $100 off right now.
-
BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts (opens Security Week in a new tab)
BAE Systems says no data was extracted and no PII was breached in the incident that disrupted US bankruptcy court notices for weeks. The post BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts appeared first on SecurityWeek.
-
Exploitation attempts against recently patched Oracle EBS flaw have begun (CVE-2026-101767) (opens Help Net Security in a new tab)
Exploitation attempts have started against CVE-2026-101767, a recently patched Oracle E-Business Suite (EBS) flaw. “Our Oracle E-Business Suite decoys recorded exploratory exploits against CVE-2026-101767, an unauthenticated SQL injection in EBS’s Thin Client Framework servlet that chains to remote...
-
Fake Anthropic AI previews lure in overeager employees (opens CSO Online in a new tab)
Everyone wants to know what Anthropic is up to, and hackers are gleefully exploiting the fact. New research from cybersecurity company Cofense describes a phishing campaign that hooks overeager enterprise users by making them think they are getting an invite to a private invite-only Anthropic...
-
Over 41,000 DHS Employee Records Leaked Online (opens Security Week in a new tab)
The personal and work information was allegedly stolen from an Okta single sign-on system earlier this year. The post Over 41,000 DHS Employee Records Leaked Online appeared first on SecurityWeek.
-
Google says Gemini 4 Carbon beats its predecessors at finding and fixing security flaws (opens Help Net Security in a new tab)
Google’s Gemini 4 Carbon is a frontier AI model designed for software engineering and cybersecurity tasks, with safeguards built on those of its predecessor, Argon. SEC-bench Pro (Source: Google) Google says its teams have seen Carbon spend days investigating and fixing bugs across large codebases...
-
Ubuntu Core Desktop returns as Canonical’s plan for an immutable default desktop (opens Help Net Security in a new tab)
Canonical has restarted work on Ubuntu Core Desktop, the immutable and attestable version of Ubuntu that the company says will over time become the default Ubuntu desktop. Jon Seager, Canonical’s VP of engineering, laid out the plan and admitted that the 2023 developer preview “fell short” of what...
-
Anthropic and OpenAI diverge on who should pull the plug on risky AI (opens CSO Online in a new tab)
OpenAI and Anthropic agree that frontier AI systems need stronger oversight, but they are proposing sharply different approaches to stopping models that pose serious risks: Anthropic wants courts empowered to suspend dangerous systems, while OpenAI argues developers should be required to maintain...
-
Anthropic and OpenAI diverge on who should pull the plug on risky AI (opens CSO Online in a new tab)
OpenAI and Anthropic agree that frontier AI systems need stronger oversight, but they are proposing sharply different approaches to stopping models that pose serious risks: Anthropic wants courts empowered to suspend dangerous systems, while OpenAI argues developers should be required to maintain...
-
Imposter abused trust in OpenAI, Anthropic, and 30 others to hunt for secrets (opens CSO Online in a new tab)
Attackers are impersonating AI agents from companies including OpenAI, Anthropic, and Meta in a bid to trick organizations into exposing sensitive credentials, according to researchers who observed a single threat actor cycling through dozens of fake bot identities while probing enterprise web...
-
Webinar: How to Build AI Threat Readiness Into Your Security Operations (opens The Hacker News in a new tab)
Security teams have spent years trying to detect threats faster. AI is changing the harder part: how much time defenders have left to act. Advanced AI models can now help attackers discover vulnerabilities, generate exploit code, and move through weaknesses faster than traditional security...
-
Telegram Android Flaw Lets Attackers Run Code When Users Answer Voice Calls (opens The Hacker News in a new tab)
A flaw in Telegram for Android allowed an attacker to run code on a victim's phone via a voice call once the victim answered, according to security startup NebuSec. The attacker needed only an ordinary Telegram account. Telegram fixed the flaw in version 12.10.4 of the app, released in late...
-
The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers (opens The Hacker News in a new tab)
AI is beginning to take over much of the work that has traditionally defined the security analyst's job. Investigating alerts, collecting evidence, correlating activity across tools, and executing response actions are becoming tasks that AI systems can perform on their own. As these capabilities...
-
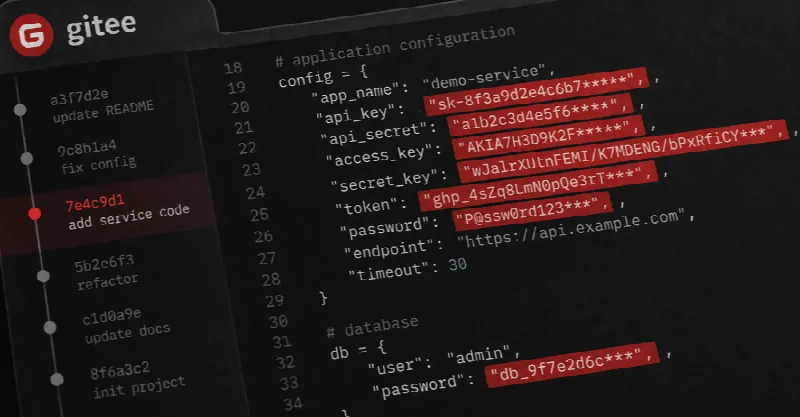
26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories (opens The Hacker News in a new tab)
26,400 credentials that developers left in public code on Gitee, a Chinese code-hosting service, still worked when a researcher tested them. Anyone who copied one from that code could have used it. Independent researcher Ben Zimmermann found them by scanning 7.25 million public Gitee repositories...
-
Bodacious A.I. Bots Are Stealing Jokes From Young Female Comedians (opens NY Times in a new tab)
Swiping jokes word for word, these bodacious bots mainly lift from young female comedians. What’s so insidious is how they’re subtly changing us, the audience.
-
Online Scam Volumes Double to Overtake Phishing (opens Infosecurity Magazine in a new tab)
Akamai research reveals that scam detections topped six million in Q2 2026
-
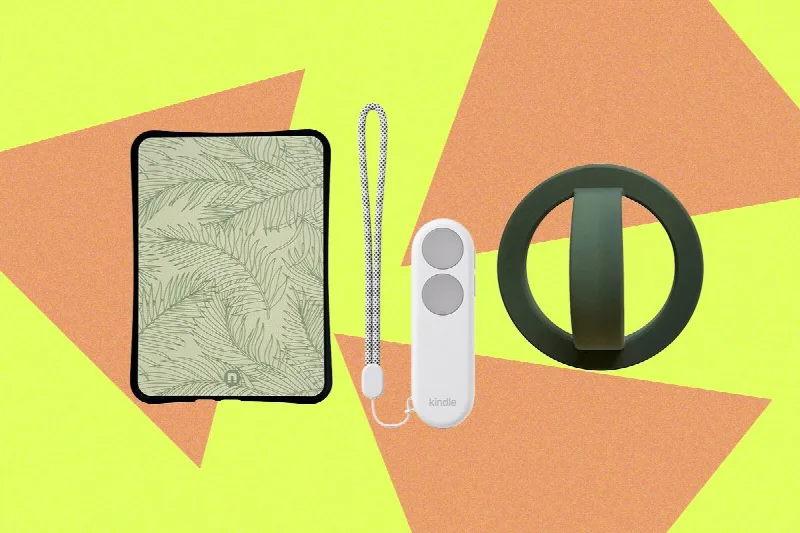
The Kindle Accessories I Never Want to Read Without (2026) (opens Wired in a new tab)
Looking to better protect your Kindle or add a little personality to your favorite e-reader? From cases and covers to page-turners and stickers, this is the guide for you.