News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Go Minimal—the Ridge Wallet is 20 Percent Off Right Now (opens Wired in a new tab)
The popular Ridge Wallet lives up to the hype and is on sale, along with other Ridge gear. Plus, you can try it risk-free for 99 days.
-
7 Entrepreneurial Skills Every Startup CTO Needs in 2027 (opens CTO Magazine in a new tab)
Your sales team needs an integration to close a deal. Engineering wants to rebuild a service that keeps failing. Your CEO wants an AI feature ready before the next funding conversation. A startup rarely has the resources to pursue every opportunity at once. The CTO must determine which investment...
-
When Risk Becomes Personal: What Security Leaders Can Learn From a Cancer Diagnosis (opens Security Week in a new tab)
Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a system or an enterprise, but you. The post When Risk Becomes Personal: What Security Leaders Can Learn From a Cancer Diagnosis...
-
Chinese hackers used VMware ESX zero-day; PHP2Shell and Fragnesia chained to root firewalls (opens Help Net Security in a new tab)
China-nexus threat actors have exploited a VMware ESX zero-day to hide their tracks and chained PHP2Shell flaws with the “Fragnesia” Linux kernel bug to root servers and firewalls, cybersecurity researchers claim. Cisco has also confirmed that attackers are crashing its firewalls with a newly...
-
Microsoft’s Profit Jumps 32% Despite Big Increase in Spending (opens NY Times in a new tab)
The company’s free cash flow stayed positive in the last quarter even as it spent $45.2 billion on capital expenses like data centers and offered to pay workers to leave.
-
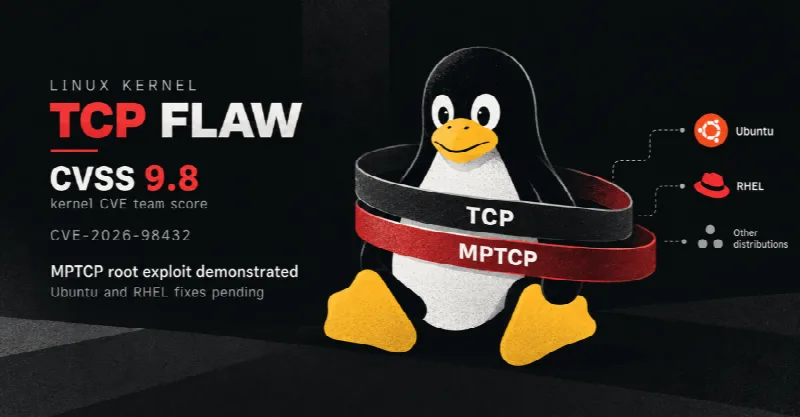
Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions (opens The Hacker News in a new tab)
A flaw in the Linux kernel's TCP code, tracked as CVE-2026-98432, affects Ubuntu, Red Hat Enterprise Linux (RHEL), and other Linux distributions. The kernel's own CVE team rates it 9.8 out of 10 on the CVSS scale. Anthropic said on October 27 that its AI model wrote an exploit that uses the flaw to...
-
Threat Modeling With 4 Simple Questions on a White Board (opens Dark Reading in a new tab)
A four-question exercise that CISOs can use to create a threat model that promises results, without a big spend.
-
Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners (opens The Hacker News in a new tab)
Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba. The activity involves creating fake GitHub projects that claim to be desktop...
-
Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model (opens Security Week in a new tab)
Google’s new frontier model scored 88.2% on SEC-bench Pro and is rolling out first to vetted cyber defenders via its Fairwind Program. The post Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model appeared first on SecurityWeek.
-
The ‘Pain in the Ass’ Math That Could Save Vibe Coding From Itself (opens Wired in a new tab)
A new startup called &Truth is joining the race to automate formal verification, a painstaking process that uses math to prove software works as intended.
-
How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI (opens Security Week in a new tab)
Unpatched voting machines, unverifiable QR-coded ballots, and AI-driven influence campaigns leave US elections short of secure. The post How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI appeared first on SecurityWeek.
-
NIK C2 Malware Can Use Victims’ OpenAI Keys for AI Queries (opens Infosecurity Magazine in a new tab)
NIK C2 malware can fall back on victims’ OpenAI API keys to run AI queries
-
Polymarket and Kalshi Turn Midterm Elections Into a Multimillion Dollar Market (opens NY Times in a new tab)
Betting markets like Polymarket and Kalshi have transformed America’s democracy into a new kind of casino.
-
Yoba malware hides in fake desktop versions of ChatGPT and Claude (opens Help Net Security in a new tab)
Fake GitHub projects posing as desktop versions of ChatGPT and Claude have been used to spread a malware chain that ends with a cryptocurrency miner, Check Point has found. The researchers have been tracking the campaign, dubbed Yoba, for the past two months. Its operator set up repositories and...
-
Amazon tells software engineers that not every task needs AI (opens IT Pro in a new tab)
The tech giant wants staff to stop tokenmaxxing and start using AI when it's sensible
-
Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps (opens Security Week in a new tab)
Cisco open sourced Project Quarry, a rule language for detecting AI agent attacks that only emerge across sequences of benign actions. The post Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps appeared first on SecurityWeek.
-
Researchers broke the browsers built into VS Code, Cursor, Copilot, Codex and Claude Desktop (opens Help Net Security in a new tab)
Forever Security found ways out of the built-in browsers in five AI coding assistants: Cursor, GitHub Copilot, OpenAI’s Codex, Microsoft’s VS Code and Anthropic’s Claude Desktop. In all five, a web page or a local file reached the computer behind the browser. Cursor ran attacker code, Copilot...
-
DoorDash to Buy Instacart for $17 Billion, Uniting 2 Delivery Giants (opens NY Times in a new tab)
The deal combines the country’s largest restaurant delivery service with its biggest online grocery platform.
-
Mistral Says Its AI Model ‘Le Chonk’ Has Leapfrogged China in the Open-Weight Race (opens Wired in a new tab)
The French AI lab claims its latest release matches or outperforms even the best models from DeepSeek and Z.ai in coding and cybersecurity.
-
CREST Urges Whole-Ecosystem Approach to Financial Cyber Resilience (opens Infosecurity Magazine in a new tab)
CREST has published a framework for strengthening cyber resilience across financial services