News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Hackers Steal 2.6 Million Records From Sony’s Japanese ISP So-net (opens Security Week in a new tab)
The data of So-net and Plala customers in Japan was exposed, along with 54,401 email account passwords and 16 bank account records. The post Hackers Steal 2.6 Million Records From Sony’s Japanese ISP So-net appeared first on SecurityWeek.
-
What are the must-have qualities of a CIO? (opens CIO Dive in a new tab)
Leaders don't need to know it all, but those capable of building trust among staff while discerning AI hype will stand out among the pack.
-
UK government targets simplified planning, community incentives with digital infrastructure build-out (opens IT Pro in a new tab)
Will the new Data Centre Covenant really make all that much difference?
-
An AI Breakthrough Has Made Decades of Computer Science Research ‘Irrelevant’ (opens Wired in a new tab)
Anthropic and OpenAI say they’ve disproved a key tenet of computer science. Researchers are struggling with the fall but also feel like “overexcited bunnies” as they look at new questions to explore.
-
Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls (opens The Hacker News in a new tab)
Cisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software that it said has been exploited in the wild. The vulnerability, tracked as CVE-2026-76418, is rated 8.6 on the CVSS...
-
NCC Group names Guy Ellis as CEO amid improved cyber profitability (opens IT Pro in a new tab)
Ellis will focus on expanding recurring revenues and scaling the firm’s cyber capabilities as it enters its next phase of growth
-
A Hacker Targeted High-Stakes Poker Players With Malware That Exposed Their Cards (opens Wired in a new tab)
Illicit software on the computers of some of the world’s best online poker players allowed the accused cheater to see what cards were in the victims’ hands—and trounce them at the tables.
-
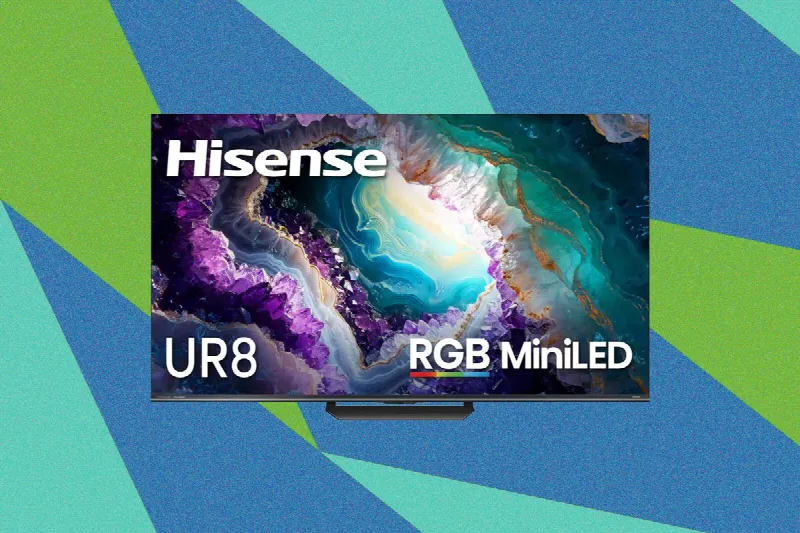
Hisense UR8 RGB MiniLED TV: Midrange Quality, Upscale Color Accuracy (opens Wired in a new tab)
The Hisense UR8 RGB MiniLED is more affordable than competitors and offers exceptional color accuracy, but is otherwise just OK.
-
ICO Reprimands Staffordshire Police After Domestic Abuse Breach (opens Infosecurity Magazine in a new tab)
The UK’s privacy regulator has issued a reprimand to Staffordshire Police following a serious breach of personal information
-
Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network (opens Security Week in a new tab)
Cisco Talos linked SD-WAN key-stealing malware to infrastructure overlapping Volt Typhoon’s Silent Train network, which Lumen detailed. The post Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network appeared first on SecurityWeek.
-
GitHub Launches npm Firewall to Block Malicious Packages Before Installation (opens The Hacker News in a new tab)
GitHub has announced that it's introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time. "The firewall inspects both metadata requests and package downloads for signs of malicious activity, acting as an install-time policy gate,"...
-
Security leaders brace for an overhaul of public key infrastructure as quantum risks rise (opens IT Pro in a new tab)
The scale of the work ahead is becoming clearer across cryptographic discovery, automation, architecture, governance and investment
-
Security leaders brace for an overhaul of public key infrastructure as quantum risks rise (opens IT Pro Security in a new tab)
The scale of the work ahead is becoming clearer across cryptographic discovery, automation, architecture, governance and investment
-
Hacktivists leak 41,000 DHS staff records, revealing undercover ICE agents (opens Help Net Security in a new tab)
Names, offices, contact details and assignments of more than 41,000 U.S. Department of Homeland Security (DHS) employees have been leaked by a hacktivist group calling itself the Department of Peace. The group handed the data to the transparency collective Distributed Denial of Secrets (DDoSecrets)...
-
Tech industry reacts to Autumn Budget 2026 (opens IT Pro in a new tab)
Investment in AI security and sovereignty capabilities have been hailed by industry stakeholders
-
I Did Push-Ups With Snap’s Chunky AR Glasses (opens Wired in a new tab)
They fit better than they look and stay put when you move, but Snap’s $2,195 Specs still feel like a developer prototype in search of a purpose.
-
When your AI vendor goes belly up (opens CIO in a new tab)
With hundreds of AI-related companies increasingly crowding the market for enterprise dollars, IT leaders should prepare for the day when at least one of their AI vendors suddenly shutters or gets acquired. While the AI market overall is showing few signs of slowing down, a shakeout will eventually...
-
Vulnerability exploitation rising as the root cause of many breaches (opens CSO Online in a new tab)
More evidence has emerged that attackers are turning to vulnerabilities rather than phishing as a means for breaking into corporate systems. Incident response firm LevelBlue’s Q3 findings show that vulnerability exploitation accounted for 14% of initial access cases, up from 4% in Q2. The finding...
-
Shadowy AI Relay Disables OpenAI Codex, Claude Code Sandboxes (opens Dark Reading in a new tab)
The enigmatic service is providing popular AI coding tools to mainland China and other regions where OpenAI and Anthropic products are not officially for sale — but with key security features turned off.
-
I Gave My Blood to the AI Death Clock (opens Wired in a new tab)
Death Clock promises to predict when you’re going to die and help you extend your time on Earth. After a month, I felt like it was sucking the life out of me.