News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Grafana Labs connects observability and incident response with Knowledge Graph (opens Help Net Security in a new tab)
Grafana Labs has announced a Knowledge Graph in every Grafana Cloud stack, alongside new Digital Experience Monitoring capabilities and updates to Grafana Cloud Incident Response Management (IRM). The releases connect infrastructure and application dependencies with user experience and incident...
-
ThreatLocker adds external controls for AI agent access and execution (opens Help Net Security in a new tab)
ThreatLocker has announced the launch of Zero Trust AI Control (ZTAIC), giving organizations a tool to deploy agentic AI without surrendering control of their environments. ZTAIC enables security teams to give AI agents exactly what they need to perform their jobs while keeping everything else out...
-
PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert (opens The Hacker News in a new tab)
This story is developing and was written before PHP's scheduled 14:00 UTC release on October 21. Once the release is out, the affected and fixed versions below are confirmed by the official advisory. PHP will ship an out-of-cycle security release at 14:00 UTC today, October 21, for two critical...
-
Children’s Data Stolen After Ransomware Attack Compromises ‘Password1’ Account (opens Infosecurity Magazine in a new tab)
The ICO has slammed security failings by the Welsh local government data unit and IT service provider following the 2024 incident
-
Attackers Abuse UpdraftCentral Keys to Plant Backdoors on WordPress Sites (opens The Hacker News in a new tab)
Unknown threat actors breached TeamUpdraft's website and potentially gained unauthorized access to customers' connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone, using them to backdoor WordPress sites. TeamUpdraft is the developer behind UpdraftPlus, a popular WordPress backup...
-
Moving past autonomous exploitation to machine-speed security (opens CSO Online in a new tab)
Frontier AI advancements have created a world where exploitation outpaces defense. The average enterprise takes 32 to 43 days to patch, but the mean time to exploit a vulnerability is 10 hours. This asymmetry creates questions around how enterprises can trust autonomous AI to operate ubiquitously...
-
The CIO’s new recovery problem: Knowing what ‘good’ looks like (opens CIO in a new tab)
For years, disaster recovery was built around a relatively simple question: How quickly can we get the business back online? That question still matters. But for today’s CIO, it is no longer enough. Enterprise technology environments have become too dynamic to define recovery simply as restoring...
-
Info-stealing malware slipped into OVHcloud CLI releases on GitHub (opens Help Net Security in a new tab)
OVHcloud, the French cloud computing and web hosting company, alerted customers that a hacker tampered with its open-source command-line interface (CLI) tool to spread information-stealing malware. OVHcloud CEO Octave Klaba disclosed the incident on X, warning users who downloaded the latest CLI...
-
Safari blocks trackers that turn your email into a tracking ID (opens Help Net Security in a new tab)
Apple’s new anti-tracking protections in Safari and WebKit, the open-source web engine used by Safari, block connections to identity resolution services that turn email addresses into persistent tracking identifiers. How email addresses become tracking IDs This “post-cookie” tracking method allows...
-
Microsoft says AI is causing a rupture between business leaders and employees (opens IT Pro in a new tab)
New Microsoft research shows a huge disconnect between leadership and employees when it comes to confidence in the UK leading in AI
-
Europe Wants Data Centers. Its Climate Goals Are Getting in the Way (opens Wired in a new tab)
A plan to funnel the heat given off by data centers into nearby homes has run aground in Germany. Across Europe, policymakers are weighing AI ambitions against climate objectives.
-
14 ways attackers abuse cloud services to hack your enterprise (opens CSO Online in a new tab)
Attackers are increasingly abusing trusted SaaS platforms, cloud infrastructure, and identity systems to blend malicious activity into legitimate enterprise traffic. Adversaries are pushing command and control (C2) through high-reputation services, including OpenAI and AWS, to blend in with normal...
-
U.S. Orders DeepSeek Removed From Federal Civilian Systems, Bans New Purchases (opens The Hacker News in a new tab)
U.S. federal civilian agencies must remove DeepSeek products from their information technology systems, along with any third-party products or services "developed using DeepSeek implementations," under a Department of Homeland Security order. They may also no longer buy information technology...
-
State Bank of India Confirms Data Leak After 3,897 Customer Records Found on Dark Web (opens The Hacker News in a new tab)
State Bank of India has identified 3,897 customer records containing personal information in a set of about 375,000 records available on the dark web, and it does not yet know where the data came from. The state-owned bank, India's largest, said in a stock-exchange filing dated October 21 that it...
-
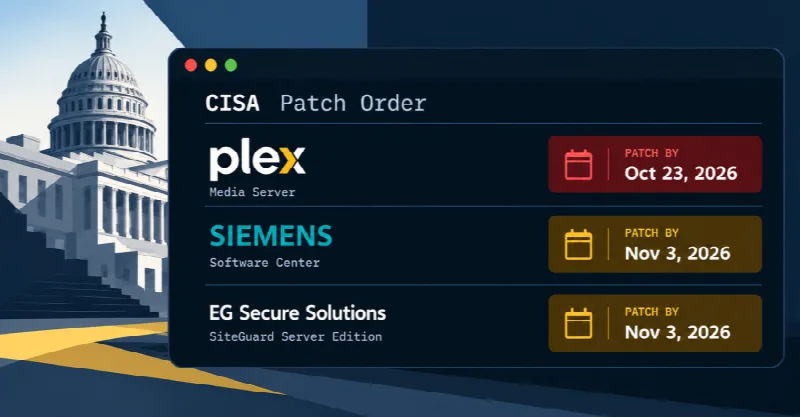
CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell. The vulnerabilities are listed below...
-
PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws (opens Security Week in a new tab)
Tracked as CVE-2026-109618 and CVE-2026-109619, the bugs could potentially lead to unauthenticated remote code execution. The post PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws appeared first on SecurityWeek.
-
Hackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare Intrusion (opens The Hacker News in a new tab)
A Belarus-aligned hacktivist group spent nearly two years within the network of a Russian healthcare organization. According to a report published by Russian cybersecurity firm Solar, the activity has been attributed to a threat cluster dubbed Partisan Zmiy, which is also known as the Cyber...
-
Hijacked Developer Account Used to Plant Stealer in OVHcloud CLI (opens Security Week in a new tab)
Researchers say the developer’s account was compromised in March with a GlassWorm-linked loader. The post Hijacked Developer Account Used to Plant Stealer in OVHcloud CLI appeared first on SecurityWeek.
-
Privacy-preserving AI can protect your heart data, the bill is the problem (opens Help Net Security in a new tab)
A heart monitor used to be a box beside a hospital bed. Electrodes fed a cable, the cable fed a screen, and a nurse watched the screen. The threat model fit on a sticky note. Cardiac care doesn’t work like that anymore. A patch or smartwatch records the electrocardiogram (ECG). A phone or gateway...
-
DevGuard: Open-source vulnerability management for the software supply chain (opens Help Net Security in a new tab)
DevGuard is a free, open source vulnerability management platform that collects a software project’s security findings in one place, ranks them by risk, and tracks them. It’s an OWASP Incubating Project, and anyone can self-host it. One command line, six scans DevGuard runs secret scanning, static...