News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
UK government urged to take stakes in publicly-funded tech firms (opens IT Pro in a new tab)
A parliamentary committee claims UKRI is failing to give taxpayers value for money
-
PHP2Shell Exploitation Attempt Detected by Amazon Four Days Before Vulnerability Disclosure (opens Infosecurity Magazine in a new tab)
Threat intelligence analysts now observe large-scale evidence of exploitation of the two critical PHP vulnerabilities
-
Cisco Patches 34 Vulnerabilities Across Multiple Products (opens Security Week in a new tab)
Critical-severity security defects could lead to command execution, authentication bypass, and XSS attacks. The post Cisco Patches 34 Vulnerabilities Across Multiple Products appeared first on SecurityWeek.
-
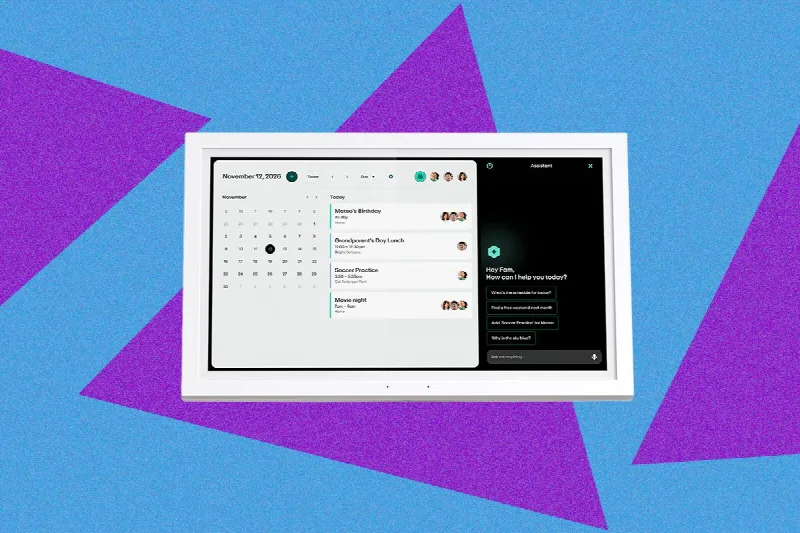
Greenlight Family Hub (2026): Finally, a Digital Wall Calendar With a Voice Assistant (opens Wired in a new tab)
After testing multiple models, I’m convinced voice control belongs on the family calendar. Greenlight’s Family Hub shows why.
-
Vendor-driven upgrades saddle IT leaders with huge ‘software tax’ (opens CIO in a new tab)
CIOs experiencing sticker shock from recent software bills should be questioning how they got there. That’s because IT leaders at large enterprises are paying a huge so-called software tax for vendor-driven upgrades, migrations, and licensing changes they would not have chosen for their...
-
Hugging Face’s New AI Biology Model Lets You Chat With DNA (opens Wired in a new tab)
The new open-source model speaks the language of DNA and can help researchers understand the effects of any changes on gene activity and health.
-
Lack of transparency leads to performative AI theater (opens CIO in a new tab)
Organizations are rapidly implementing AI, but employees often feel left behind about how AI is changing their roles. While AI can help get work done faster, it won’t necessarily help produce better quality work if employees aren’t confident in their AI skills. In fact, a recent survey from...
-
Building the agent and securing it (opens CIO in a new tab)
Earlier this year, I wrote about how vibe coding an AI governance platform forced me to rethink governance itself. Building agents took the problem much further. When I built the platform, I was the operator. I described what I wanted. The model generated code. I tested it. That loop was fast...
-
PHP2Shell Exploitation Started Days Before Patches (opens Security Week in a new tab)
Initial attempts were observed on October 17, and mass activity began shortly after patches were released. The post PHP2Shell Exploitation Started Days Before Patches appeared first on SecurityWeek.
-
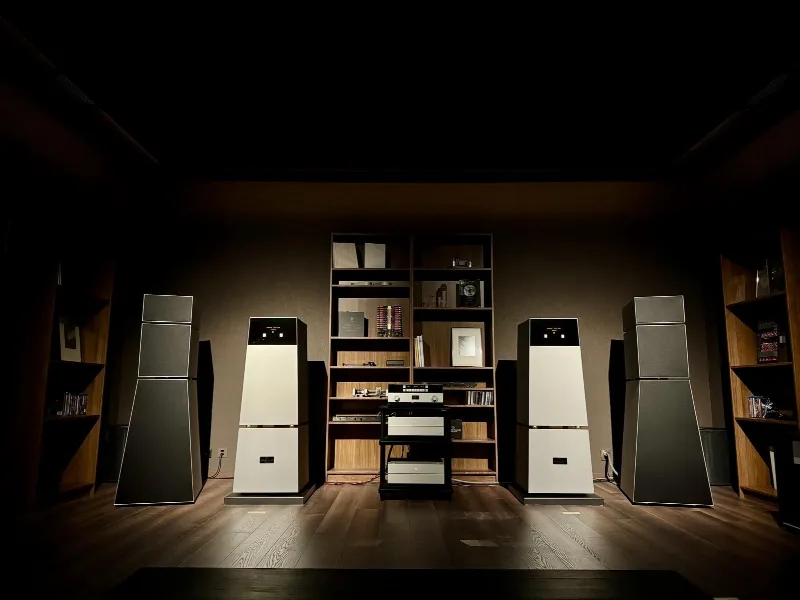
This Preamp Costs More Than a Fancy Sports Car (opens Wired in a new tab)
Goldmund’s $240,000 Mimesis Statement is an exercise in extreme Swiss sound engineering—and only one part of a $1.5 million audio setup.
-
HPE eyes infrastructure flexibility gains with new Private Cloud AI announcements at GTC Berlin (opens IT Pro in a new tab)
New GPU flexibility features will support a “broader mix of AI workloads” for HPE Private Cloud AI users
-
HPE eyes infrastructure flexibility gains with new Private Cloud AI announcements at GTC Berlin (opens IT Pro Cloud in a new tab)
New GPU flexibility features will support a “broader mix of AI workloads” for HPE Private Cloud AI users
-
The AI boom is putting construction at the centre of the digital economy (opens CIO in a new tab)
For the past two years, the conversation around AI has focused on which industries it will disrupt. But AI’s rapid growth is also creating a major infrastructure challenge. As investment pours into data centres and supporting infrastructure, the AI boom is becoming central to delivering the next...
-
LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release (opens The Hacker News in a new tab)
LiteLLM on Wednesday disclosed that threat actors compromised "multiple independent security controls" to push a malicious version of the Python package containing a credential stealer and a backdoor. On October 21, 2026, LiteLLM's release pipeline was compromised to push 1.107.0 to the Docker Hub...
-
Cloud Security Maturity Lags Despite Widespread Adoption, SANS Warns (opens Infosecurity Magazine in a new tab)
Nearly all organizations now run production workloads in the cloud, but a new SANS survey found most have yet to achieve mature cloud security programs
-
Node.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported Versions (opens The Hacker News in a new tab)
Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in the Brotli decompression code that Node.js bundles, which the project says can allow remote code execution, meaning an attacker could run code of...
-
Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU (opens Security Week in a new tab)
Nearly 100 vulnerabilities have been assigned a critical severity rating and Fusion Middleware received the most patches. The post Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU appeared first on SecurityWeek.
-
Meta Ordered to Pay New Mexico $25 Billion for Deceiving Users About Privacy on Facebook (opens Security Week in a new tab)
The $25 billion award far exceeds a $5 billion fine the Federal Trade Commission levied against Facebook in 2019. The post Meta Ordered to Pay New Mexico $25 Billion for Deceiving Users About Privacy on Facebook appeared first on SecurityWeek.
-
SAP AI NOW: Follow the keynote live from the NEC (opens IT Pro in a new tab)
Find out more about the latest insight and research live from the Birmingham NEC
-
Why AI security is rapidly becoming one of the biggest commercial opportunities for the channel (opens IT Pro Security in a new tab)
AI security presents an opportunity for the channel to tap into recurring revenue