News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Stop sending me engineers: what OpenAI, Anthropic and Microsoft misread about enterprise AI (opens CIO in a new tab)
The AI industry says enterprises can’t absorb AI. Its answer is to absorb it for them. That’s not the same thing. The engineer across the table knew the model cold. Not vendor-deck cold. He could tell me where it would break, what it would cost, and which benchmark numbers to ignore. One of the...
-
UK Government Announces Sweeping New AI Security Plans (opens Infosecurity Magazine in a new tab)
The government is planning tweaks to legislation, new incident response and more to head of AI security threats
-
Cyberattack Prompts Grocery Giant Ahold Delhaize to Disconnect Systems (opens Security Week in a new tab)
The company says it took some of its systems offline to contain a security issue within its network. The post Cyberattack Prompts Grocery Giant Ahold Delhaize to Disconnect Systems appeared first on SecurityWeek.
-
Meta outlines Muse Wonder safeguards for AI agents acting on your behalf (opens Help Net Security in a new tab)
Meta’s Muse Wonder and Muse Wonder Full models are built for AI agents that handle tasks such as preparing insurance claims, reviewing leases and developing software. The models combine document analysis and tool use with the ability to retain relevant details across conversations and work through...
-
SAP customers seek renewed control over their ERP fate (opens CIO in a new tab)
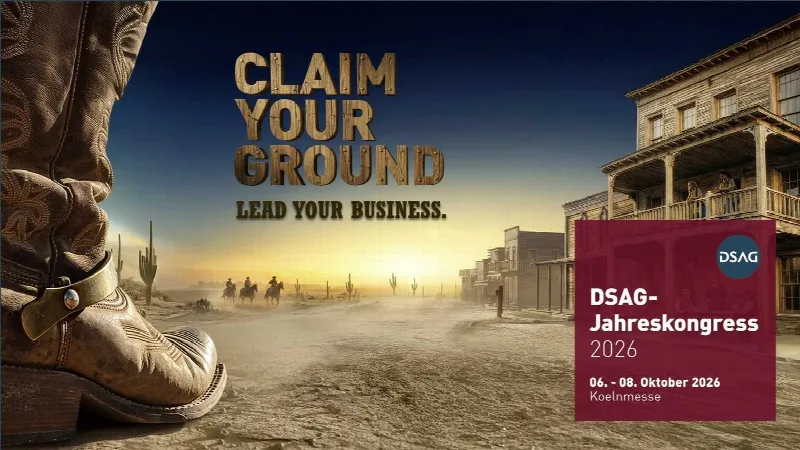
“Claim your ground, lead your business” is the overarching motto of this year’s German-speaking SAP User Group (DSAG) congress — a slogan the organizers say aims to bring SAP’s technological vision in line with the concrete challenges faced by its customers, complete with a striking Western motif...
-
SAP customers seek renewed control over their ERP fate (opens CIO in a new tab)
“Claim your ground, lead your business” is the overarching motto of this year’s German-speaking SAP User Group (DSAG) congress — a slogan the organizers say aims to bring SAP’s technological vision in line with the concrete challenges faced by its customers, complete with a striking Western motif...
-
GitLab admins urged to patch critical RCE flaw (CVE-2026-97229) (opens Help Net Security in a new tab)
GitLab is urging users of self-managed instances to patch a critical vulnerability (CVE-2026-97229) in its CI/CD Regular Expression Compiler that could allow remote attackers to execute arbitrary code on GitLab servers. About CVE-2026-97229 CVE-2026-97229 is an integer overflow vulnerability in...
-
6 Best Coffee Grinders Based on Particle Analysis and Tasting (2026) (opens Wired in a new tab)
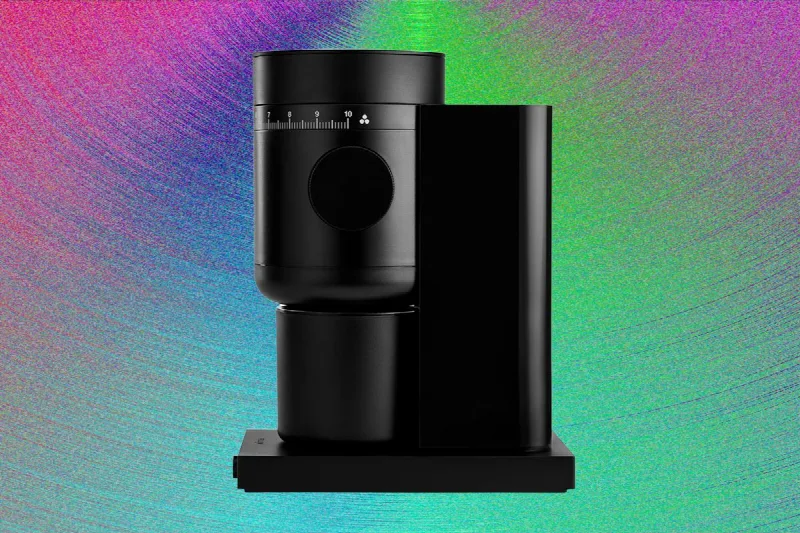
We used particle size analysis and real-world testing to find the best conical burr, flat burr, and blade grinders for every budget and style of coffee drinker.
-
npm Trusted Publishing flaw exposed 1,500+ npm packages to takeover (opens Help Net Security in a new tab)
Bloom Security researchers found that npm’s Trusted Publishing feature let an attacker push new versions of someone else’s package without stealing a credential. The attacker only needed to register a GitHub repository name the maintainer had left behind. Bloom counted more than 1,500 npm packages...
-
What Flock Actually Costs Cities Across the Country (opens Wired in a new tab)
WIRED examined contracts from over two dozen cities and towns that shed light on how Flock’s pricing and business model functions, and how it stacks up against its peers.
-
Fifth of CISOs Take Time Off to Avoid Patch Tuesday (opens Infosecurity Magazine in a new tab)
Socura report claims CISOs are calling in sick or taking holiday to miss Patch Tuesday
-
AI’s hidden choices — and why getting them right avoids lock-in (opens CIO in a new tab)
The first wave of enterprise AI deployments was straightforward: a chat interface calling a model, wrapped around a few clear use cases. The next wave is driven by autonomous agents that maintain state, revisit context, call tools and act under real permissions. This means enterprise AI teams must...
-
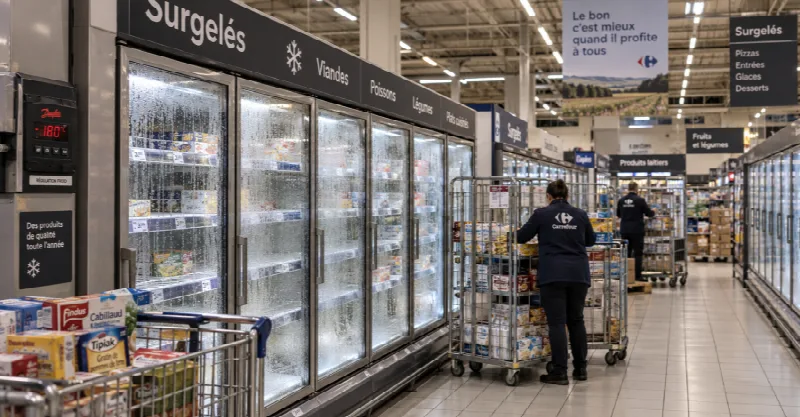
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers (opens The Hacker News in a new tab)
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The attackers reached them through the controller that runs all of a store's fridges and freezers, a...
-
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control (opens The Hacker News in a new tab)
Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says. Progress published all 31 on October 12 and scored five of them critical. Fixes have been available...
-
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code (opens The Hacker News in a new tab)
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. "GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to...
-
Refrigeration Controller Hack Spoils Food Across European Supermarkets (opens Security Week in a new tab)
A cyberattack targeted refrigeration controllers, setting refrigerators and freezers across hundreds of supermarkets to defrost. The post Refrigeration Controller Hack Spoils Food Across European Supermarkets appeared first on SecurityWeek.
-
BlueStar to be acquired by distribution giant TD Synnex (opens IT Pro in a new tab)
The proposed acquisition is expected to create new market opportunities for customers, partners, and vendors
-
What is Beyond Zero? The latest Google-backed security trend explained (opens IT Pro Security in a new tab)
Zero Trust has been a fixture of modern organizations for many years, but experts worry we need something more robust in the AI era
-
Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies (opens The Hacker News in a new tab)
Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devices into residential proxies. The activity, which targets Android devices built on MediaTek platforms across several...
-
Be a good AI ancestor: Cybersecurity already gave us the playbook (opens Help Net Security in a new tab)
AI has brought us to a familiar inflection point in the story of privacy, cybersecurity, and online safety. We have an opportunity to apply decades of cybersecurity experience before the next generation of technology creates consequences we cannot easily reverse. I learned the importance of that...