News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Fake AI Attacks Spread Across US Companies: How MSSPs Can Stop Incidents Early (opens The Hacker News in a new tab)
Attackers are impersonating popular AI products to distribute malware, steal browser sessions, and compromise business accounts. ANY.RUN linked 1,258 public sandbox analyses to fake AI campaigns between April and October of 2026. The campaigns also increase operational pressure on MSSPs serving US...
-
Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation (opens The Hacker News in a new tab)
Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8.6), is a case of remote code execution in the management interface. "A remote code execution (RCE)...
-
Europe must invest in its own AI companies or be left at the mercy of the US and China, says Mistral AI co-founder (opens IT Pro in a new tab)
“AI isn’t the internet” warns Arthur Mensch, as he encourages Europe to take a more active role in AI’s development
-
LiteLLM flaws allow full admin control and API-key theft (opens IT Pro in a new tab)
Users are advised to implement patch immediately in order to avoid breaches
-
LiteLLM flaws allow full admin control and API-key theft (opens IT Pro Security in a new tab)
Users are advised to implement patch immediately in order to avoid breaches
-
Ransomware extortion gets personal as attackers target employees’ families (opens CSO Online in a new tab)
Ransomware attackers are expanding their tactics beyond encrypting corporate systems and threatening to leak stolen data. They are increasingly using AI in attacks, exploiting organizations’ own AI systems and even using physical intimidation by threatening employees and their families to pressure...
-
EU can't afford sovereign cloud, research claims (opens IT Pro in a new tab)
Citing costs that it claims have been overlooked, CCIA Europe is predicting a €115 billion bill.
-
Warning Over High-Risk Vulnerabilities in Widely Used LLM Gateway Tool (opens Infosecurity Magazine in a new tab)
CVE-2026-35029 and CVE-2026-59823 affect LiteLLM, which is commonly used by enterprises to connect their AI applications to providers like OpenAI and Anthropic
-
CikaBika Bot RAT Uses Discord for C&C (opens Security Week in a new tab)
Delivered via phishing, the malware provides reconnaissance, remote execution, and data exfiltration capabilities. The post CikaBika Bot RAT Uses Discord for C&C appeared first on SecurityWeek.
-
Why AI Confidence Is Not Validation (opens The Hacker News in a new tab)
AI is already part of digital forensics and incident response work, with or without a policy in place to govern it. The issue is that these tools are growing more confident in their own output faster than practitioners are developing reliable ways to verify it. Without governance models and...
-
Kids’ Content Is Deeply Broken. A New Platform Wants to Fix It (opens Wired in a new tab)
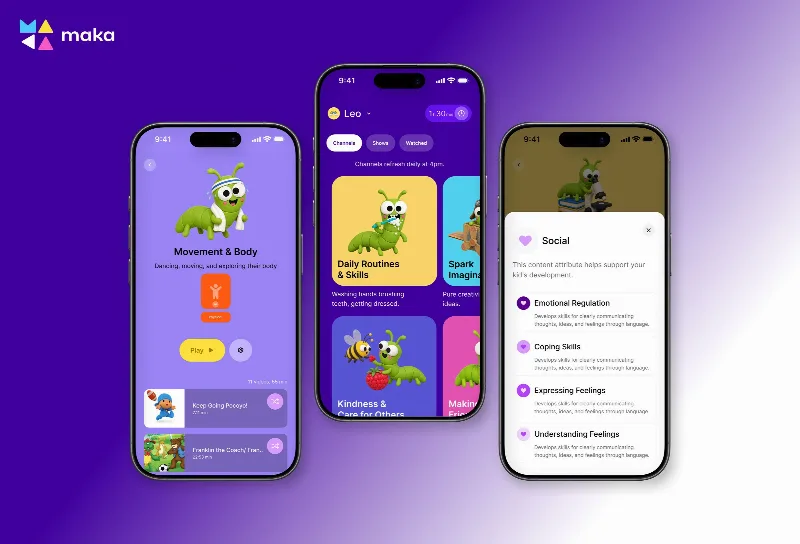
Low-quality AI-generated content currently dominates children’s media. Maka, a streaming platform run by child development experts, is offering an alternative.
-
What a cockatoo can teach us about the evidence AI wasn’t built to hear (opens CIO in a new tab)
AI systems do not make decisions from reality. They make decisions from representations of reality: records, observations, measurements, histories, labels, documents, and whatever else an organization has decided belongs in the data. That distinction sounds almost too obvious to be interesting, yet...
-
Top banks reckon with AI risks, but spot benefits (opens CIO Dive in a new tab)
“We’re not going to allow just any outside agent to come inside the company because that’s just too risky,” JPMorgan Chase CEO Jamie Dimon said.
-
Exhausted Parents Are Turning to A.I. Apps Despite the Risks (opens NY Times in a new tab)
Even as alarm grows over the risks, families are embracing bots and agents to tackle the spiraling administrative tasks of modern child rearing.
-
CISA flags exploited flaws in Palo Alto, Cisco and Ahsay products (opens Help Net Security in a new tab)
The US Cybersecurity and Infrastructure Security Agency (CISA) has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-0322, a high-severity remote code execution (RCE) vulnerability in the management interface of Palo Alto Networks PAN-OS CVE-2026-76519, a...
-
Bank of America hired 1,000 security consultants to address Mythos-spotted flaws (opens IT Pro in a new tab)
Temp hires were needed to work through patches and other fixes necessary to address vulnerabilities spotted by the AI security models
-
Bank of America hired 1,000 security consultants to address Mythos-spotted flaws (opens IT Pro Security in a new tab)
Temp hires were needed to work through patches and other fixes necessary to address vulnerabilities spotted by the AI security models
-
India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1 (opens The Hacker News in a new tab)
The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers' registered names along with their numbers for incoming calls starting November 1, 2026, in an effort to help people identify calls from unknown numbers and tackle spam or fraudulent...
-
Democrats Are Gearing Up to Investigate the Trump Administration. It Won’t Be Easy (opens Wired in a new tab)
As a recent government report on DOGE shows, even getting basic information out of the Trump administration will put a new Congress to the test.
-
Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies (opens Security Week in a new tab)
The Hirudo malware combines elements of a traditional banking trojan and a full-featured RAT. The post Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies appeared first on SecurityWeek.