News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
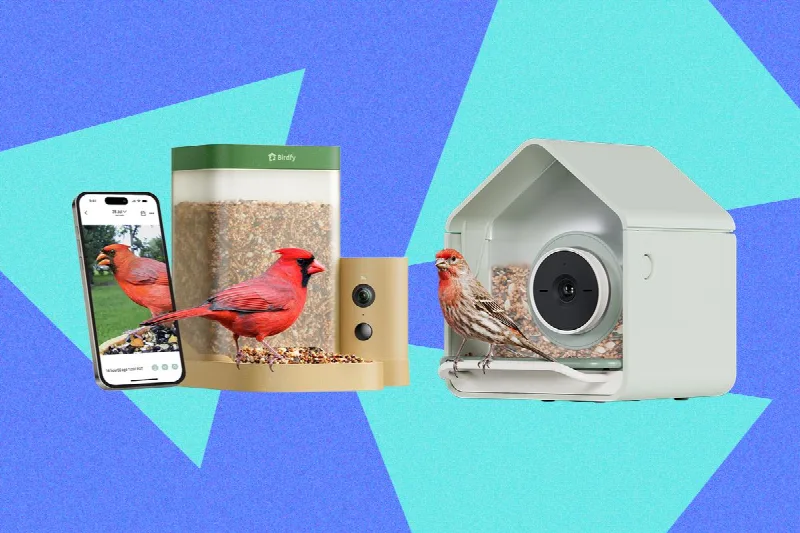
Birdbuddy vs. Birdfy: Which Budget Smart Feeder Should You Buy? (2026) (opens Wired in a new tab)
I tested Birdbuddy’s Nook and Birdfy’s Rookie in my backyard. Saving money comes with compromises, but some are easier to live with.
-
Bitter Deploys PapRAT in Asian Cyber-Espionage Campaign (opens Infosecurity Magazine in a new tab)
Bitter used three infection chains against South and Southeast Asian targets, one with no malware executable
-
National Grid plans massive new substation to support Teesside data center plans (opens IT Pro in a new tab)
Dorman Point is expected to come online by the end of 2029 with an initial 1,440 MVA capacity
-
Revolve Data Breach Impacts at Least 180,000 People (opens Security Week in a new tab)
Hackers accessed its online shopping platform and stole customers’ personal and payment card information. The post Revolve Data Breach Impacts at Least 180,000 People appeared first on SecurityWeek.
-
Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward (opens Security Week in a new tab)
The top payout is for high-impact architectural research demonstrating full administrative control. The post Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward appeared first on SecurityWeek.
-
Infostealer uses LLMs to compile dossiers on victims (opens IT Pro in a new tab)
Volta-Autodoxer collates and evaluates data from passwords to Uber Eats receipts
-
Infostealer uses LLMs to compile dossiers on victims (opens IT Pro Security in a new tab)
Volta-Autodoxer collates and evaluates data from passwords to Uber Eats receipts
-
Salesforce acquires Rune Technologies to add offline capabilities to Missionforce (opens CIO in a new tab)
Salesforce is in the process of acquiring US-based defense-tech startup Rune Technologies to add offline capabilities to Missionforce, its Agentforce avatar for national security, defense, aerospace, and government agencies. The startup’s TyrOS platform will be used to extend Missionforce into...
-
Trezor warns some of its wallets may hide a seed-stealing implant (opens Help Net Security in a new tab)
A Trezor Safe 5 sold by CryptoBilis, the reseller linked to the recent Ledger wallet drains, may contain a hidden implant that steals the owner’s recovery phrase, Trezor has warned. Trezor is a Czech company and part of SatoshiLabs Group. It has made hardware wallets since 2014, and its current...
-
A compromised DevOps laptop caused the $6.3B Binance breach (opens CSO Online in a new tab)
Cryptocurrency Exchange Binance blamed a compromised DevOps laptop for the loss of $6.3 billion in cryptocurrency last week, adding that it will now cover any losses faced by its customers. “Binance will cover all losses from the Secure Assets Fund for Users (SAFU) and the company’s funds,” the...
-
When You Should—and Shouldn’t—Use AI to Search the Web (opens Wired in a new tab)
Chatbots are often quite good at retrieving the information you want from the web. But sometimes you’ll get better results by typing your query into a good old search engine.
-
18 Best Gifts for PC Gamers (2026): Headsets, Desks, Monitors (opens Wired in a new tab)
Shopping for a PC gamer? This is the gear we use ourselves, starting at prices as low as $12.
-
Heineken CIO uses AI to operationalize data-driven decisions (opens CIO Dive in a new tab)
Use cases tailored to solve specific problems within the business and a cautiously governed rollout have generated AI value, Frank Iannella said.
-
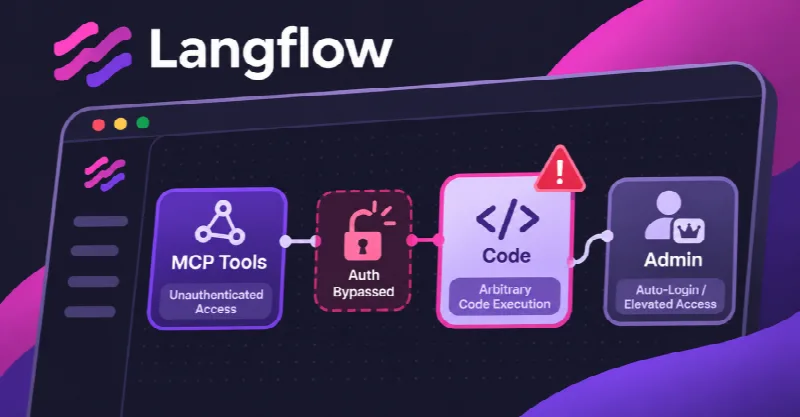
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers (opens The Hacker News in a new tab)
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an open-source tool for building AI agents and workflows, and its vulnerability reports go to IBM. Every release from 1.0.0 through 1.12.8 has the...
-
Chainalysis breached using “offensive agentic techniques” (opens Help Net Security in a new tab)
Blockchain analytics firm Chainalysis has suffered a cybersecurity incident that led to a data breach. According to the company’s Friday announcement, the incident is unrelated to the recent Binance hack. What was accessed? In October, the company detected external attackers using “offensive...
-
Cursor removes malicious Claude Code extension after SSH backdoor attempt (opens CSO Online in a new tab)
A malicious version of Anthropic’s Claude Code extension distributed through the Cursor marketplace attempted to install a persistent Secure Shell (SSH) backdoor on developers’ machines, potentially giving attackers remote access to systems holding source code, credentials and other sensitive...
-
Want to Sign With a Hollywood Agent? Start Making Fun of AI (opens Wired in a new tab)
Even as studios incorporate generative tech into film and TV production, comedy content creators have broken through by roasting chatbots.
-
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy (opens The Hacker News in a new tab)
Forty percent of security teams now use AI every day, and another 56% are testing it. Only 4% have no plans to adopt it, according to Prophet Security's State of AI in Security Operations 2026 survey of more than 250 CISOs, SOC leaders and practitioners. For the teams still testing, the next...
-
Malicious Claude Code Extension Served in Cursor Supply Chain Attack (opens Security Week in a new tab)
The extension performed host reconnaissance and attempted to create a reverse SSH tunnel. The post Malicious Claude Code Extension Served in Cursor Supply Chain Attack appeared first on SecurityWeek.
-
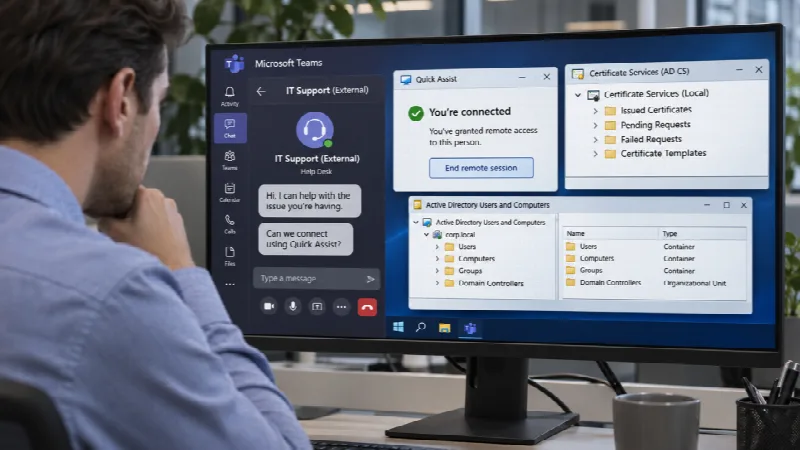
Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data (opens The Hacker News in a new tab)
Attackers posing as IT support on Microsoft Teams talked employees into giving them remote control of their PCs. They then used insecure Active Directory Certificate Services (AD CS) settings to obtain login certificates for privileged accounts, including one for a domain controller. Microsoft said...