News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Open-weight AI models are changing the equation. Here’s what CIOs should experiment with next (opens CIO in a new tab)
For years, enterprise AI strategy has been dependent on a small set of proprietary, closed model providers, a limitation that has carried cost, lock-in and opacity. Now, open-weight models from Meta, Google and other global competitors are challenging that default. As of July 2026, open-weight...
-
Attackers Exploit Third Arista VCO Zero-Day in Four Months (opens Security Week in a new tab)
The critical-severity SQL injection flaw allows attackers to access privileged internal functionality and gain operator privileges. The post Attackers Exploit Third Arista VCO Zero-Day in Four Months appeared first on SecurityWeek.
-
Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image (opens The Hacker News in a new tab)
Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open. The flaw, CVE-2026-112900, is in the way Pillow handles EPS images, which it opens by passing the file's name to Ghostscript, a...
-
Best Early Black Friday Smart Bird Feeder Deals (2026) (opens Wired in a new tab)
I’ve spent years testing smart bird feeders. These are the currently discounted models I’d buy for myself—or give as gifts.
-
8 Things to Know About the iPhone Duo (opens Wired in a new tab)
Did you manage to score Apple’s first folding phone on launch day? Are you still mulling it over? Here are a few things to keep in mind.
-
Capcom data breach exposes 11.7 million account records (opens Help Net Security in a new tab)
Players who signed up for Capcom’s online account service may want to look twice at emails that seem to come from the company. The company has disclosed that a third party gained unauthorized access to customer information linked to CAPCOM ID, the account people use to sign in to the company’s web...
-
Best Dyson Week Deals (2026): Dyson V15 Detect, Dyson Airwrap (opens Wired in a new tab)
Dyson’s sale event is happening now, and you can save up to $300 on vacuums, hair tools, and more.
-
Enterprises are being stung by unexpected AI bills, and it’s disrupting IT budgets (opens IT Pro in a new tab)
A survey by Cisco found that observability costs are skyrocketing amid the shift to AI, despite half unable to measure LLM response quality
-
The ‘Mythos moment’ has already passed. Now comes the hard part for cybersecurity (opens CSO Online in a new tab)
When Anthropic introduced Claude Mythos Preview, the cybersecurity debate quickly turned to what AI could do: uncover decades-old vulnerabilities, develop working exploits and accelerate tasks that once required specialist expertise. Anthropic noted that Mythos discovered software flaws no human...
-
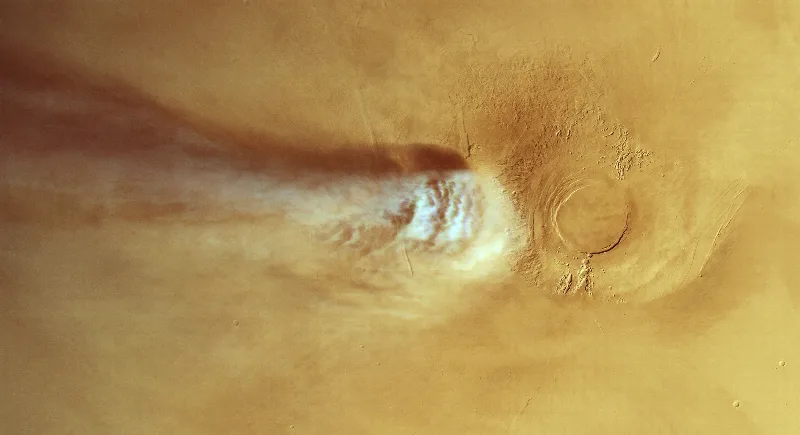
The ‘Exotic Physics’ Behind a Mysterious 1,000-Mile Cloud on Mars (opens Wired in a new tab)
The cloud has baffled astronomers since its discovery in 2018. Now, a new study offers a possible cause for its appearance.
-
Your AI is only as good as the network underneath it (opens CIO in a new tab)
When an AI workload is not performing as expected, the obvious place to look is the GPU. Do we have enough compute capacity? Would adding more GPUs solve the problem? Not necessarily. The GPUs may be perfectly capable of handling the workload, but if the network is not able to move data quickly and...
-
Researchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli Data (opens The Hacker News in a new tab)
Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their "Node2Shell" proof of concept ran code on the official Node.js 24.22.0 image for Linux arm64, with no debugger or custom build, by...
-
Critical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token Balances (opens The Hacker News in a new tab)
AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious API asked for it, security firm V12 said on October 22. The cause was the SDKs' default client, which set no spending limit until releases on August 18 added one. The...
-
11 Million Impacted by Capcom Data Breach (opens Security Week in a new tab)
The hackers stole 11 million email addresses from CAPCOM ID and changed the login passwords for 196 accounts. The post 11 Million Impacted by Capcom Data Breach appeared first on SecurityWeek.
-
Quest Diagnostics Data Breach Exposed ‘Certain Patient Records’ (opens Security Week in a new tab)
In a regulatory filing, Quest Diagnostics reported unauthorized access to its Quanum Lab Services Manager, a platform where certain clients can place test orders. The post Quest Diagnostics Data Breach Exposed ‘Certain Patient Records’ appeared first on SecurityWeek.
-
The AI notetaker risk is now an everywhere problem (opens CSO Online in a new tab)
The businesspeople adopting AI notetakers are not being reckless. They are responding to a real business need. Our teams are in meetings all day with companies we support, and the idea that we could read a clean summary of every one of them at the end of the day makes us better partners to our...
-
Hackers hijack exposed AI models to launch cyberattacks at victims’ expense (opens Help Net Security in a new tab)
An attack tool built around AI goes looking for AI models that anyone on the internet can reach, then uses them to plan break-ins while the model’s owner pays for the computing power. Symantec captured the agent’s instruction set this summer through a honeypot posing as an unprotected AI service...
-
LiteLLM Compromised in Fresh Supply Chain Attack (opens Security Week in a new tab)
Hackers used compromised GitHub CLI OAuth tokens to push and approve malicious packages on PyPI and Docker. The post LiteLLM Compromised in Fresh Supply Chain Attack appeared first on SecurityWeek.
-
Atlassian Patches 75 Flaws in Data Center and Server Products (opens Security Week in a new tab)
Atlassian’s October bulletin lists 176 vulnerability entries, including 14 critical-severity issues, all in third-party components. The post Atlassian Patches 75 Flaws in Data Center and Server Products appeared first on SecurityWeek.
-
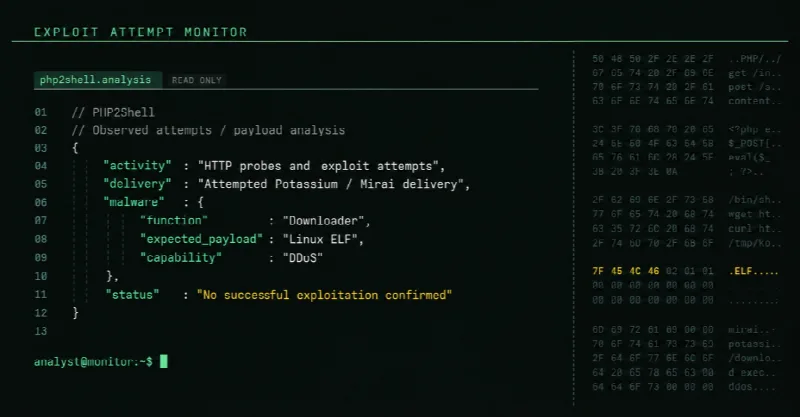
PHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai Malware (opens The Hacker News in a new tab)
Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges that weaponizing the flaws may be harder than previously thought. The attacks aim to exploit...