News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Hammer Distribution and Acronis partner on automated MSP cyber operations (opens IT Pro in a new tab)
Hammer channel partners can now access Acronis’ portfolio of cybersecurity, infrastructure, and AI solutions
-
eMudhra quits global TLS certificate market after compromise of CA signing keys (opens CSO Online in a new tab)
Indian digital trust company eMudhra has announced that it is exiting the global SSL/TLS certificate business and is offering customers certificates issued by Sectigo as an alternative, following the compromise of private keys behind eight of its intermediate certificate authorities. The company’s...
-
China APT Uses AI Pentest Tool Artex in ConnectWise Attacks (opens Security Week in a new tab)
The state-sponsored hackers targeted hundreds of organizations and gained privileged access to some environments. The post China APT Uses AI Pentest Tool Artex in ConnectWise Attacks appeared first on SecurityWeek.
-
TDM Neo Hybrid Headphones Review: Two-in-One Woes (opens Wired in a new tab)
CES 2026 loved these innovative headphones that transform into a Bluetooth speaker. After living with them, I’m impressed by the engineering, but less impressed by the sound.
-
Widespread Token-Spraying Attacks Target Microsoft 365 Accounts For Email Compromise (opens Infosecurity Magazine in a new tab)
Security researchers identified attempts to access corporate networks which have been linked to a major Microsoft 365-targeted BEC campaign using phishing, stolen session tokens and social engineering
-
Big tech taskforce unveils new blueprint for UK AI leadership (opens IT Pro in a new tab)
Success depends on deeper collaboration between government, industry, local leaders and communities
-
A Dating App Is Offering ‘Chivalry Mode’ and ‘Marriage Timeline’ to Get Gen Z Married (opens Wired in a new tab)
Upward, a newly relaunched Christian app, is pitching trad values to a generation that barely even dates.
-
What Type of Mattress Is Right for You? (2026) (opens Wired in a new tab)
Here’s how to pick the best mattress for your sleep needs, straight from a professional mattress tester.
-
AI ‘Tokenomics’ is a trap. CIOs should avoid it at all costs. (opens CIO in a new tab)
According to a quartet of Accenture intellectual heavyweights, what CIOs need now to account for and control AI costs is tokenomics, sweet tokenomics. The idea of linking AI spend to business outcomes may be a noble one, but “Tokenomics” only pretends to do so, unless you think tallying costs and...
-
Attacks on Tech Firms Behind Most Third-Party Data Breach Victims (opens Infosecurity Magazine in a new tab)
Kroll found that 69% of data breach victims in the past year were affected by a third-party breach, with attacks on tech companies the most common cause
-
Are polymath profiles the key to AI success? (opens CIO in a new tab)
AI has a cross-cutting impact on businesses. It’s changing operations, management, and even decision-making processes. But it’s also modifying what they expect from their teams and how they’re organized. This has a direct impact on the decisions of both HR departments and CIOs, who must now...
-
Open-weight AI models are changing the equation. Here’s what CIOs should experiment with next (opens CIO in a new tab)
For years, enterprise AI strategy has been dependent on a small set of proprietary, closed model providers, a limitation that has carried cost, lock-in and opacity. Now, open-weight models from Meta, Google and other global competitors are challenging that default. As of July 2026, open-weight...
-
Attackers Exploit Third Arista VCO Zero-Day in Four Months (opens Security Week in a new tab)
The critical-severity SQL injection flaw allows attackers to access privileged internal functionality and gain operator privileges. The post Attackers Exploit Third Arista VCO Zero-Day in Four Months appeared first on SecurityWeek.
-
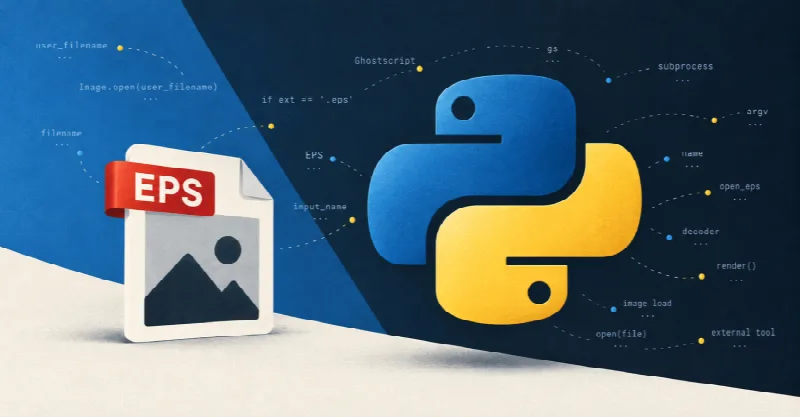
Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image (opens The Hacker News in a new tab)
Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open. The flaw, CVE-2026-112900, is in the way Pillow handles EPS images, which it opens by passing the file's name to Ghostscript, a...
-
Best Early Black Friday Smart Bird Feeder Deals (2026) (opens Wired in a new tab)
I’ve spent years testing smart bird feeders. These are the currently discounted models I’d buy for myself—or give as gifts.
-
8 Things to Know About the iPhone Duo (opens Wired in a new tab)
Did you manage to score Apple’s first folding phone on launch day? Are you still mulling it over? Here are a few things to keep in mind.
-
Capcom data breach exposes 11.7 million account records (opens Help Net Security in a new tab)
Players who signed up for Capcom’s online account service may want to look twice at emails that seem to come from the company. The company has disclosed that a third party gained unauthorized access to customer information linked to CAPCOM ID, the account people use to sign in to the company’s web...
-
Best Dyson Week Deals (2026): Dyson V15 Detect, Dyson Airwrap (opens Wired in a new tab)
Dyson’s sale event is happening now, and you can save up to $300 on vacuums, hair tools, and more.
-
Enterprises are being stung by unexpected AI bills, and it’s disrupting IT budgets (opens IT Pro in a new tab)
A survey by Cisco found that observability costs are skyrocketing amid the shift to AI, despite half unable to measure LLM response quality
-
The ‘Mythos moment’ has already passed. Now comes the hard part for cybersecurity (opens CSO Online in a new tab)
When Anthropic introduced Claude Mythos Preview, the cybersecurity debate quickly turned to what AI could do: uncover decades-old vulnerabilities, develop working exploits and accelerate tasks that once required specialist expertise. Anthropic noted that Mythos discovered software flaws no human...