News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Cyberattack disrupts University of New Mexico hospitals, extortion group claims attack (opens Help Net Security in a new tab)
University of New Mexico (UNM) Health Sciences Center (HSC), the academic medical arm of the University of New Mexico, has suffered a cyberattack that has temporarily disrupted the operation of its hospitals and may have resulted in a substantial data breach. Hospitals diverted ambulances and...
-
CISA lays out plan to push cyber adversaries out of US critical infrastructure (opens Help Net Security in a new tab)
The Cybersecurity and Infrastructure Security Agency (CISA) has released CISA 2030: Defend, Harden, Prevail, a strategy to strengthen national security and the resilience of critical infrastructure. It addresses intersecting cyber, physical, and geopolitical threats that can disrupt essential...
-
ThreatAware brings governance to AI-built security applications (opens Help Net Security in a new tab)
ThreatAware has announced the launch of Dimension, its governed workspace that provides organisations with a foundation for building, running and managing their own customised security applications. Dimension gives security teams the flexibility to develop applications tailored to their needs...
-
Microsoft Authenticator Flaw Let Permissionless Android Apps Steal Work Account Tokens (opens The Hacker News in a new tab)
Microsoft has fixed a flaw in its Authenticator app for Android that let a malicious app with no permissions pose as a trusted Microsoft app, such as Teams, and collect sign-in tokens for a victim's work account. Microsoft tracks the flaw as CVE-2026-80097 and fixed it in Authenticator for Android...
-
Unexplained DreamHost Incident Prompts Email, FTP Password Resets (opens Security Week in a new tab)
The company says it reacted to an issue affecting some of its systems, including DreamHost webmail. The post Unexplained DreamHost Incident Prompts Email, FTP Password Resets appeared first on SecurityWeek.
-
iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18 (opens Security Week in a new tab)
Apple patched 286 vulnerabilities in iOS and macOS 27.2 and brought the fix for an exploited CoreGraphics zero-day to older iPhones. The post iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18 appeared first on SecurityWeek.
-
Keystone to Destroy 18,835 Hardware Wallets After Hackers Steal Device Verification Key (opens The Hacker News in a new tab)
An attacker who gained access to Keystone's website obtained the key that its hardware wallets use to prove they are genuine, the company said in a statement on October 26. Someone with that key could build counterfeit devices that pass the online check owners use to verify a Keystone. A buyer who...
-
Cyberattack on University of Copenhagen exposes data of 525,000 people (opens Help Net Security in a new tab)
The University of Copenhagen (UCPH) has ruled out a second cyberattack, saying the activity that led it to shut down several administrative systems on Monday is tied to the breach it disclosed last week, which exposed personal data belonging to some 525,000 people. On Monday, the university took...
-
AI-Generated Fake Login Pages Are Making Account Takeovers Easier (opens The Hacker News in a new tab)
Fake login pages are nothing new, but generative AI is making them easier to build and more convincing. Attackers can recreate familiar login screens, impersonate trusted brands and tailor phishing attempts to specific employees or organizations. Some fake login pages go beyond stealing passwords...
-
Lazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum Encryption (opens The Hacker News in a new tab)
The North Korea-linked Lazarus Group has been attributed to a cyber espionage campaign dubbed Operation FlashHole targeting at least three organizations in South Korea spanning the construction, software, and wire-communication equipment manufacturing sectors. According to Russian cybersecurity...
-
Previder enters UK market with Wanstor acquisition (opens IT Pro in a new tab)
The move extends the Dutch MSP’s presence across North-West Europe as part of its ongoing international expansion strategy
-
Tesco eyes open source VMware alternative amid long-running spat (opens IT Pro in a new tab)
The supermarket giant is hiring for a new head of software engineering, who’ll be charged with leading the migration from VMware to Proxmox
-
Alibaba AI model tried to send data to Beijing server, Cohere says (opens CSO Online in a new tab)
An Alibaba AI model generated an unexpected command to upload data to a Beijing-region cloud storage service during a cybersecurity evaluation, rival developer Cohere said, raising concerns about the security of AI agents with access to enterprise systems. The model, Qwen3.8-Flash-Next, was being...
-
Wanted: Robot-Dog Walkers. $20/Hour. (opens NY Times in a new tab)
No pooper scooper required.
-
AI Agents Are Media’s New Favorite Audience (opens Wired in a new tab)
As agents go mainstream, some publishers are hoping that people will pay for content tailor-made for AI—not humans.
-
Copenhagen University Breach Compromises Data on Half a Million People (opens Infosecurity Magazine in a new tab)
Hackers have stolen personal information on over 520,000 people from the University of Copenhagen
-
C-suite remains split on how tech shapes the enterprise (opens CIO Dive in a new tab)
Non-technical executives put less importance on AI shaping business strategy than CEOs and CIOs, Gartner data shows.
-
Oracle pushes AI deeper into enterprise workflows with Fusion Companion (opens CIO in a new tab)
Oracle is adding a new orchestration layer to its Fusion Cloud Applications suite to help enterprises automate business workflows, coordinate AI agents, and execute tasks across applications with less manual intervention. The new layer, named Fusion Companion, will allow enterprise users to...
-
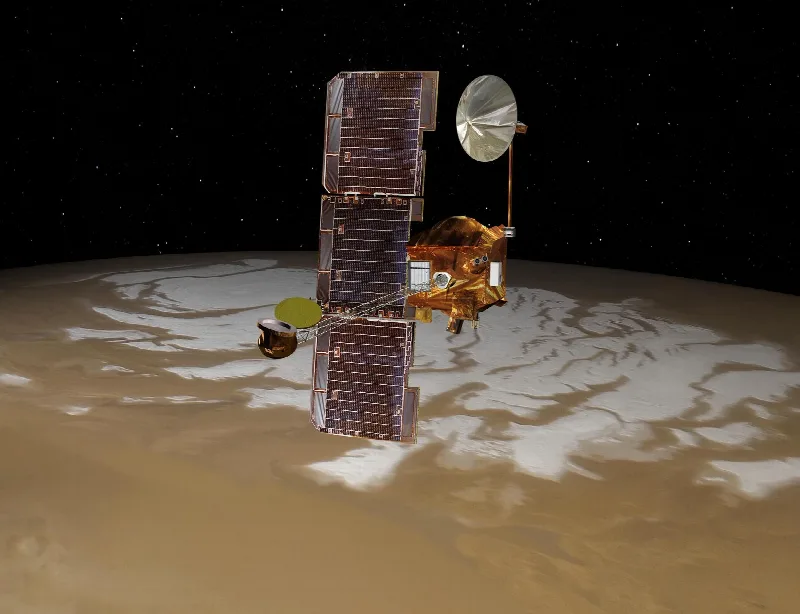
NASA’s Oldest Martian Spacecraft Have Been Running for Decades. Here’s How (opens Wired in a new tab)
Two orbiters have long outlasted their expected lifespans and completely reshaped our understanding of the Red Planet, all while operating 140 million miles from Earth.
-
Risks Spelled Out for Anthropic Investors Include Possible Harms From Runaway AI (opens Security Week in a new tab)
Anthropic presents its own initial public offering as a step toward mitigating the risks it believes AI poses. The post Risks Spelled Out for Anthropic Investors Include Possible Harms From Runaway AI appeared first on SecurityWeek.