News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
ICE Is Running One of the Largest Anti-Left Surveillance Operations in US History (opens Wired in a new tab)
ICE’s Homeland Security Investigations is engaged in far-reaching spying against left-wing activists that rivals the FBI and CIA crackdowns on the Civil Rights and anti-war movements.
-
Hackers Start Probing Fresh Oracle EBS Vulnerability (opens Security Week in a new tab)
CVE-2026-101767 is an unauthenticated SQL injection that can be exploited for remote code execution. The post Hackers Start Probing Fresh Oracle EBS Vulnerability appeared first on SecurityWeek.
-
Your AI agents have audit logs. Can you reconstruct their decisions? (opens CIO in a new tab)
The moment arrives after the damage. An agent has cancelled a supplier contract, approved a refund it should have declined or moved a customer record somewhere it should never have gone. Someone senior asks a simple question. Why did it do that? The engineering team opens the logs. There are...
-
'Britain risks becoming a vassal state' without bold AI sovereignty plans (opens IT Pro in a new tab)
UKAI said the government's approach to AI sovereignty is too fragmented, and is calling for a unified plan
-
CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts (opens Security Week in a new tab)
CISA added the Brotli flaw to its KEV catalog, and two honeypot operators logged attempts, including one that used a broken exploit. The post CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts appeared first on SecurityWeek.
-
Westcon-Comstor targets EMEA channel growth with Palo Alto Networks initiative (opens IT Pro in a new tab)
The Partner Growth Circle provides joint planning and specialist support to help partners grow their Palo Alto Networks business
-
AI Emergency Alerts Are Coming. Humans Might Not Be Ready (opens Wired in a new tab)
Human beings struggle with emergency communication. Chatbots can help—if people take them seriously.
-
10 ways attackers abuse AI services to hack your business (opens CSO Online in a new tab)
Attackers are starting to exploit AI systems to mount attacks in the same way they once relied on built-in enterprise tools such as PowerShell. Instead of relying on malware, cybercriminals are increasingly abusing AI tools enterprises depend on — a trend some experts describe as “living off the AI...
-
89% of enterprises have scaled back AI deployments over token costs (opens IT Pro in a new tab)
Volatile token costs across 2026 have caused major headaches for IT leaders
-
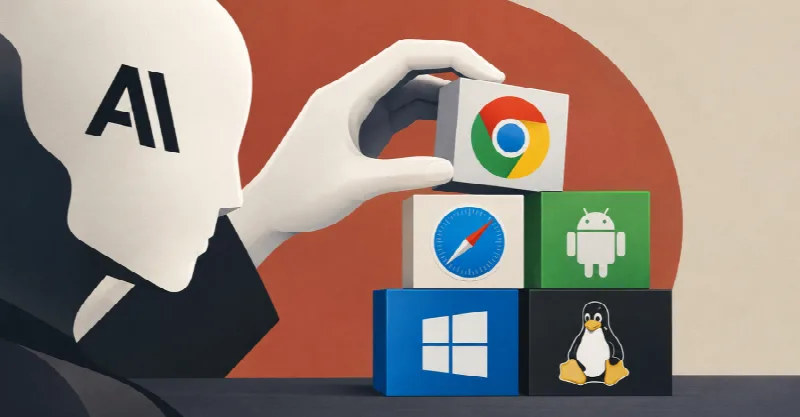
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits (opens The Hacker News in a new tab)
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The exploits were built in the lab after the model was prompted, not seen in any real attack, and...
-
What enterprises can learn from Anthropic’s IPO prospectus about vendor dependency (opens IT Pro Cloud in a new tab)
With the Claude creator set to go public in November, there are lessons to be learned about the risks of single-vendor dependency
-
FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering (opens The Hacker News in a new tab)
The U.S. Department of Justice (DoJ) on Tuesday announced the seizure of a domain associated with a bulletproof hosting provider (BPH) named Virtualine. The move was in response to the service being used to commit and facilitate prolific criminal activity, including "the advertisement of sexually...
-
Japan's GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach (opens The Hacker News in a new tab)
Japan's GMO Internet Group is offering up to $1 million in total for tips that help catch the attackers who breached its Onamae.com Desktop Cloud service, after refusing to pay an extortion demand. The reward program opened on October 28 and pays only if a tip helps lead to an arrest or an...
-
Tailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other Servers (opens The Hacker News in a new tab)
Tailscale has released version 1.104.4 to fix flaws in its built-in SSH server that could let an attacker reach services and files on other servers that only the root user should be able to touch. The flaws are in how Tailscale SSH forwards network connections, a job the Tailscale background...
-
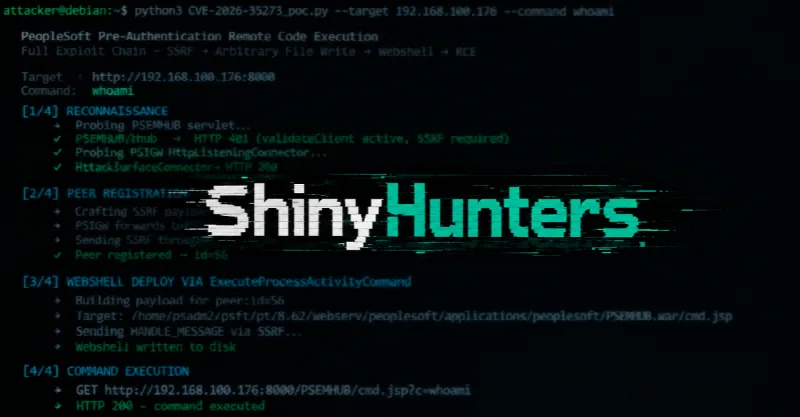
ShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained Flaws (opens The Hacker News in a new tab)
The critical Oracle PeopleSoft bug that ShinyHunters has exploited since May is not one flaw but three chained together, the researchers who reported it said this week. Oracle patched all three under a single identifier, CVE-2026-35273, in June. Its root is a server-side request forgery (SSRF) that...
-
Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature (opens Dark Reading in a new tab)
Interpol's annual Operation Serengeti, now on its third iteration, led to 1,462 arrests across 20 African countries and the US, recovering $105 million in stolen funds.
-
Should AI Decide Your Court Case? This Judge Says Yes (opens Wired in a new tab)
One of England’s top judges, Geoffrey Vos, believes that AI could adjudicate plenty of civil cases. The question, he says, is where the line should be drawn.
-
Adobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic Emerges (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added two vulnerabilities impacting Adobe Commerce and Magento, and Google's Brotli decoder library to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are...
-
Attackers compromised 42 GitHub repositories by using files too large to be searched (opens CSO Online in a new tab)
A security research firm reported Monday that it had identified breaches of 42 third-party GitHub repositories in which attackers had deployed payload blobs large enough “to evade the GitHub search and API paths normally used to find this kind of compromise.” The report from JFrog Security Research...
-
Attackers built a ‘Skynet’ AI agent that hijacks exposed models to run cyberattacks (opens CSO Online in a new tab)
Skynet is no longer a fictional adversary. Attackers have built an offensive agent that exploits unprotected AI models on the web with a ‘Skynet’ directive that allows them to run unattended for up to 100,000 steps. In this mode, a reference to the humanity-destroying artificial neural...