News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild (opens The Hacker News in a new tab)
The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild. The vulnerability in question is CVE-2026-48842 (CVSS score: 8.1), a pre-authentication SQL injection in the virtuser_query plugin of Roundcube Webmail...
-
OpenAI and Anthropic could withhold new AI models from UK's AI Security Institute (opens IT Pro in a new tab)
The move marks the second time Anthropic declined to submit a model for testing in the space of a month
-
OpenAI and Anthropic could withhold new AI models from UK's AI Security Institute (opens IT Pro Security in a new tab)
The move marks the second time Anthropic declined to submit a model for testing in the space of a month
-
RemControl Banking Trojan Gives Attackers Remote Control of Android Devices (opens Infosecurity Magazine in a new tab)
The newly-discovered trojan abuses the Android Accessibility Service to gain control over victim devices and collect sensitive banking credentials
-
How CISA plans to shake up the CVE program (opens IT Pro in a new tab)
CISA will sharpen its focus on program governance, ecosystem participation, data infrastructure, and CVE record content
-
How CISA plans to shake up the CVE program (opens IT Pro Security in a new tab)
CISA will sharpen its focus on program governance, ecosystem participation, data infrastructure, and CVE record content
-
Nutanix snaps up Ryax Technologies to strengthen enterprise AI initiatives (opens IT Pro in a new tab)
Ryax’s advanced GPU utilization and smart scheduling capabilities will be integrated into the Nutanix Kubernetes Platform
-
Researchers Identify AliExpress Phishing Domains Before Registration (opens Infosecurity Magazine in a new tab)
EfficientIP says it flagged AliExpress phishing domains before they were registered
-
Fixing Flock: The controls needed now that misuse patterns are clear (opens CSO Online in a new tab)
Flock Safety has stirred widespread debate of late. Flock builds interconnected networks of automated license-plate readers and other public safety cameras. Those systems can help police solve serious crimes, but they also log sensitive personal location data and make it searchable across agencies...
-
Nearly half of CISOs have been hit by AI deepfake voice calls (opens IT Pro in a new tab)
Gartner has urged CISOs to remain vigilant for voice and video social engineering attacks
-
Nearly half of CISOs have been hit by AI deepfake voice calls (opens IT Pro Security in a new tab)
Gartner has urged CISOs to remain vigilant for voice and video social engineering attacks
-
Russia's Hybrid Cyber-Physical War in Europe Heats Up (opens Dark Reading in a new tab)
A storm is raging in the form of cyber sabotage, disinformation, and drone attacks on European nations, particularly those that provide material support to Ukraine.
-
What to expect at NetApp Insight 2026 (opens IT Pro Cloud in a new tab)
NetApp will have to convince customers that it's still the go-to provider despite rising costs
-
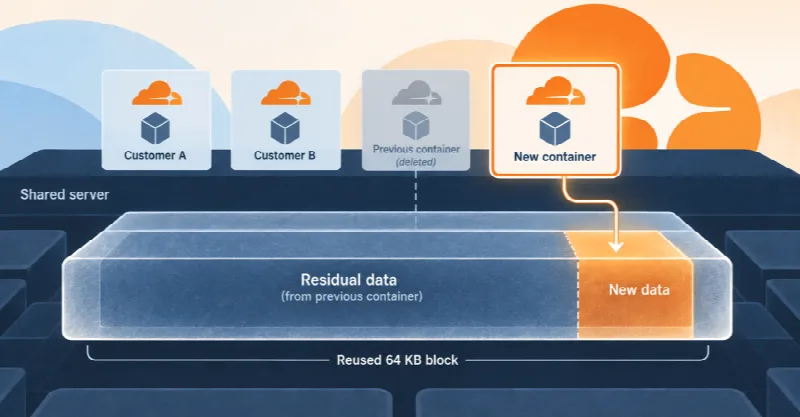
Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data (opens The Hacker News in a new tab)
A flaw in Cloudflare Containers let a paying customer read data that other customers' containers had left behind on the same server, Cloudflare and the researchers who found it said on Thursday. The data came from disk space that earlier containers had used and given up, not from any live workload...
-
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added two critical security flaws impacting WSO2 and Adobe Commerce and Magento to its Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active exploitation. The vulnerabilities are listed below...
-
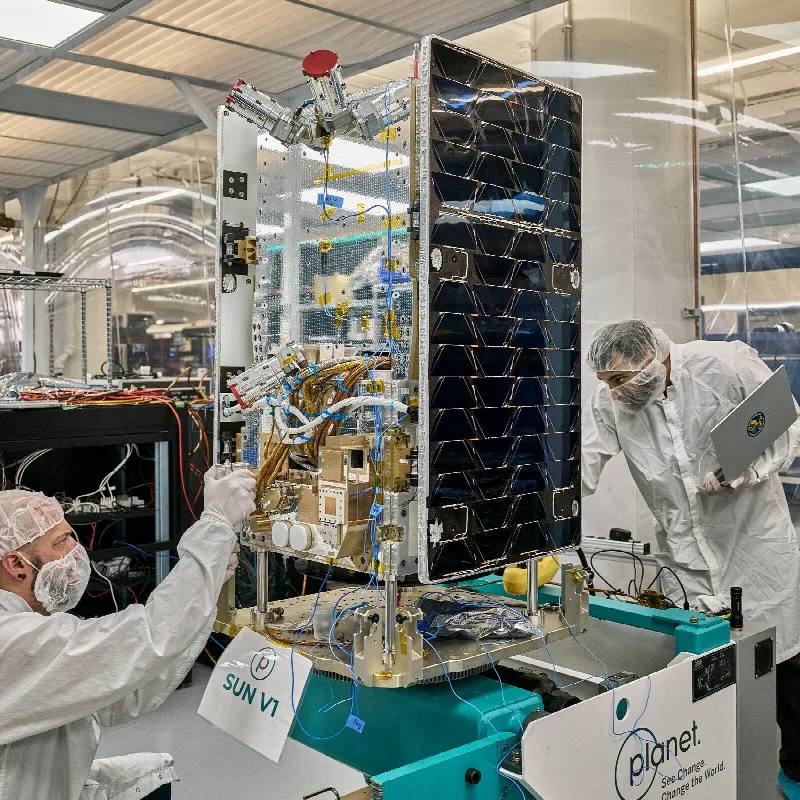
Can Tech Companies Like Google Really Put Data Centers in Space? (opens NY Times in a new tab)
Google is preparing to launch a satellite that can run its A.I. technologies from the heavens. But this is just a first step.
-
U.S. Intercedes for Elon Musk’s X Over European Fine (opens NY Times in a new tab)
Federal officials asked to intervene in a case that accused the social media platform of allowing deceptive behavior on its site and resulted in a $140 million penalty.
-
Elizabeth Holmes to Transfer to Halfway House in August 2027 (opens NY Times in a new tab)
The founder of the blood-testing start-up Theranos was sentenced to 11 years in prison for fraud and had been serving time at a minimum-security federal prison in Texas.
-
'Salesbleed' Exploits Salesforce Agents to Enable Slack Phishing (opens Dark Reading in a new tab)
Agentic AI can smuggle arbitrary instructions from the Web, across multiple apps, into trusted internal communications channels.
-
SectopRAT Returns, Hiding Inside a Legitimate Application (opens Dark Reading in a new tab)
The latest activity from the remote access Trojan (RAT) shows why organizations should monitor the behavior of applications rather than blindly trusting them, experts say.