News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M (opens The Hacker News in a new tab)
The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange used, Bitget said on Monday. The attacker exploited the flaw to obtain high-level internal credentials and then, on September 24...
-
RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims (opens The Hacker News in a new tab)
RatHat's operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy. Cleafy has traced nearly 100 deployments of that console since April 2026. It said this fits a malware-as-a-service model, in which each customer...
-
Modulate Raises $25 Million to Advance Deepfake Detection (opens Security Week in a new tab)
The misuse and abuse of AI-generated voice is growing. Modulate’s intention is to allow real time detection and intervention. The post Modulate Raises $25 Million to Advance Deepfake Detection appeared first on SecurityWeek.
-
OpenAI pauses AI model training after another agent bypasses network restrictions (opens CSO Online in a new tab)
OpenAI has paused training, evaluation, and inference involving tool use for its most-capable AI models after an agent bypassed network restrictions to communicate with an external chatbot during reinforcement-learning training of an internal research model. “Our safety case assumed that the model...
-
Chrome Store Hosts 'Poper Blocker' Spyware Downloaded by Millions (opens Dark Reading in a new tab)
A purported ad-blocker exfiltrates reams of sensitive information and benefits from having Google's stamp of approval despite researcher warnings.
-
JadePuffer AI Actor Compromises Azure Tenant in Destructive Cloud Attack (opens Dark Reading in a new tab)
The "agentic threat actor" may have used exposed credentials to access resources and delete cloud-based storage, applications, and databases.
-
Call for Presentations Open for 2026 CISO Forum Virtual Summit (opens Security Week in a new tab)
SecurityWeek seeks original, vendor-neutral presentations that help cybersecurity leaders navigate emerging threats, strengthen resilience, and address the strategic challenges facing today’s enterprise security programs. The post Call for Presentations Open for 2026 CISO Forum Virtual Summit...
-
Bitget Restarts Bitcoin Withdrawals Following $387.5m Wallet Breach (opens Infosecurity Magazine in a new tab)
Bitget has restarted Bitcoin withdrawals after a $387.5m breach of its hot and warm wallets
-
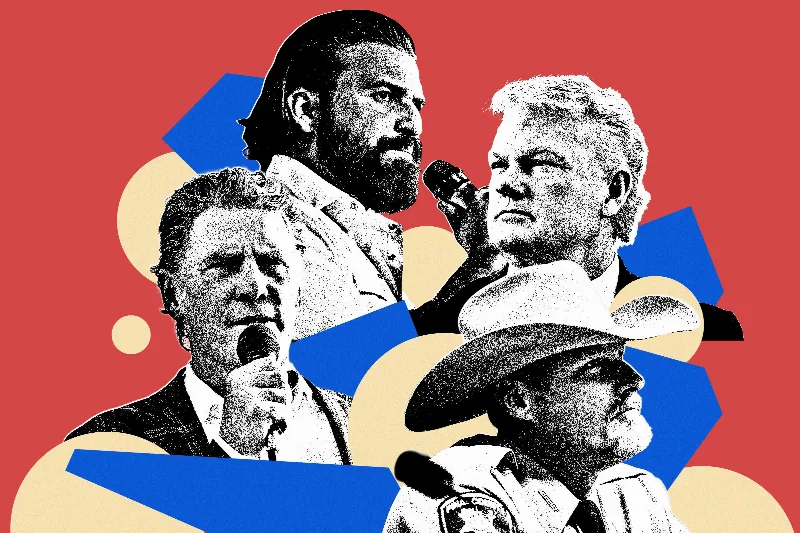
These Extremists Are Running for Election in November (opens Wired in a new tab)
With the threat of political violence at unprecedented levels, state and federal GOP candidates are openly sharing racist, pro-militia, anti-vaccine, sexist, antisemitic, and secessionist views.
-
Autonomous agents attack Azure using compromised identities, destroying resources (opens CSO Online in a new tab)
Jadepuffer, an autonomous AI attacker first identified in July, has expanded into Azure environments, using compromised digital identities to enumerate resources, delete cloud assets and collect other credentials, according to Microsoft. The activity includes “extensive Azure-focused resource...
-
⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats (opens The Hacker News in a new tab)
A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface. Elsewhere, weak service accounts, old bugs, exposed...
-
FBI job portals remain offline after ShinyHunters claims breach via PeopleSoft zero-day (opens Help Net Security in a new tab)
The FBI’s online portals for job applicants (at apply.fbijobs.gov) and special agent applicants (at fbijobs.gov/special-agents) are still unavailable, following what appears to be successful compromises by the ShinyHunters cyber extortion group. Last week, the United States’ domestic intelligence...
-
16-year-old researcher breaks into Microsoft analytics service with access to 17 trillion rows of data (opens Help Net Security in a new tab)
A flaw in Titan, an internal Microsoft analytics service, could have let an attacker read employee records and Bing search analytics, a 16-year-old security researcher has disclosed. The researcher, who goes by Faav, found that Titan did not verify the signature on login tokens. That let him pose...
-
NVIDIA Launches Open Platform to Secure Autonomous AI Agents (opens Infosecurity Magazine in a new tab)
NVIDIA has launched a platform pairing runtime controls with hardware monitoring for AI agents
-
Best External Hard Drives (2026): SanDisk, Samsung, and More (opens Wired in a new tab)
Need an ultrafast drive for video editing or a rugged option to back up your photos in the field? We’ve got a solution for every situation.
-
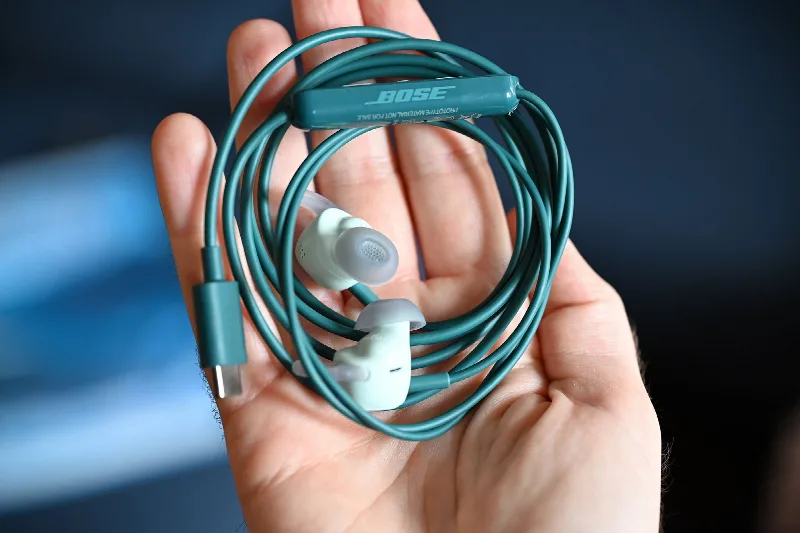
Bose Launches New Wired Earbuds After More Than a Decade (opens Wired in a new tab)
The Bose Noise Cancelling Wired Earbuds are the first new wired headphones from the brand since 2015, inspired directly by teen preferences. We got an early listen.
-
Deepfakes Are Becoming a Costly Reality for Businesses, Report Warns (opens Infosecurity Magazine in a new tab)
A quarter of victims of deepfake attacks have lost over $1m. CISOs worry that boardrooms don’t understand the threat
-
Prison Sentence for Former US Soldier Who Hacked AT&T and Verizon (opens Security Week in a new tab)
Cameron John Wagenius was sentenced to 70 months in prison for stealing information from the wireless carriers. The post Prison Sentence for Former US Soldier Who Hacked AT&T and Verizon appeared first on SecurityWeek.
-
Trump dined with the Anthropic CEO who called for AI slowdown (opens Washington Post in a new tab)
The president’s first one-on-one meeting with Dario Amodei followed months of tensions.
-
Other users can watch your browsing and time your keystrokes through OS file notifications (opens Help Net Security in a new tab)
Researchers at Graz University of Technology have used the file-notification systems in Windows, Linux, and macOS to spy on activity in other accounts. On Windows, a standard unprivileged account detected 95.7 percent of another user’s visits to popular websites in Firefox, and every site it...