News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
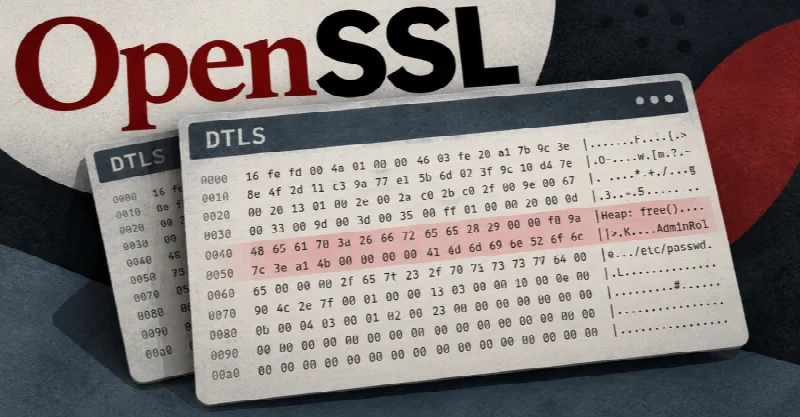
OpenSSL Fixes High-Severity DTLS Flaw That Can Leak Heap Memory Unencrypted (opens The Hacker News in a new tab)
A High-severity OpenSSL flaw can leak heap memory to the other side of a DTLS connection or crash the program, OpenSSL said on September 29 as it released fixes. DTLS, the TLS variant used for UDP traffic, resends a handshake message if no reply arrives before the timer expires. The leak or crash...
-
AI gets more interesting when it meets the physical world (opens The Next Web in a new tab)
A transporter pulls up to a construction site outside Riyadh, unloads a delivery of bulk cement, and sends a photo of the delivery note through WhatsApp. For most of BRKZ’s history, that photo was the start of a chain of human work. Someone had to read the document, find the matching order, verify...
-
Meta expands Instagram’s School Partnership Program in the US (opens The Next Web in a new tab)
Meta is adding new features to Instagram’s School Partnership Program in the US, allowing schools and verified high school students to share news about clubs, sports teams, and events, the company announced. The update arrives a month after Meta’s settlement with US states over claims that it...
-
Former US Air Force members behind million-dollar BEC scheme head to prison (opens Help Net Security in a new tab)
Two men who ran BEC and phishing campaigns against US businesses while serving in the Air Force have been sentenced to a combined 189 months in federal prison. According to public documents and evidence presented at sentencing, Chijioke Timothy Odimegwu, 25, and Harafat Mogaji, 26, both from...
-
South Africa Seeks Help After Cyberattack Targets Air Traffic Control (opens Dark Reading in a new tab)
As aviation infrastructure suffers more cyberattacks, air traffic systems are the latest target, with a ransomware toolkit installed on at least one operational network.
-
High-Severity Vulnerabilities Patched in OpenSSL, WolfSSL (opens Security Week in a new tab)
Roughly a dozen vulnerabilities have been patched in each of the open source cryptographic libraries. The post High-Severity Vulnerabilities Patched in OpenSSL, WolfSSL appeared first on SecurityWeek.
-
Genea brings AI agents to access control with role-based permissions (opens Help Net Security in a new tab)
Genea has announced the release of Genea MCP, a Model Context Protocol (MCP) server that connects AI agents directly to the Genea Access Control platform. Onboarding a new hire, setting up a contractor for two weeks, or unlocking the loading dock now takes one sentence instead of a dozen clicks...
-
Mistral CEO tells CNBC US AI safety debate covers rivals’ ‘negligence’ (opens The Next Web in a new tab)
Mistral chief executive Arthur Mensch said the US debate over AI safety has been a cover for the “negligence” of some of his rivals. He made the comments to Annette Weisbach in an interview with CNBC on Tuesday. “The debate that we’ve seen in the U.S. has been a cover for the negligence of some […]...
-
Security tools can now scan Claude Enterprise chats and uploads for sensitive data (opens Help Net Security in a new tab)
More than 100 security and compliance vendors have integrations with the Claude Compliance API, which lets a company send Claude activity into the monitoring tools it already uses. CrowdStrike, Microsoft Purview, Splunk, Palo Alto Networks, Cloudflare and Zscaler are among them. For a Claude...
-
OWASP Noir: Open-source static analysis tool (opens Help Net Security in a new tab)
OWASP Noir is an open-source static analysis tool that reads an application’s source code and lists the endpoints it exposes: paths, HTTP methods, parameters, headers, and cookies, each tied to the file and line it came from. Here’s where it gets useful. Shadow APIs, the endpoints that live in the...
-
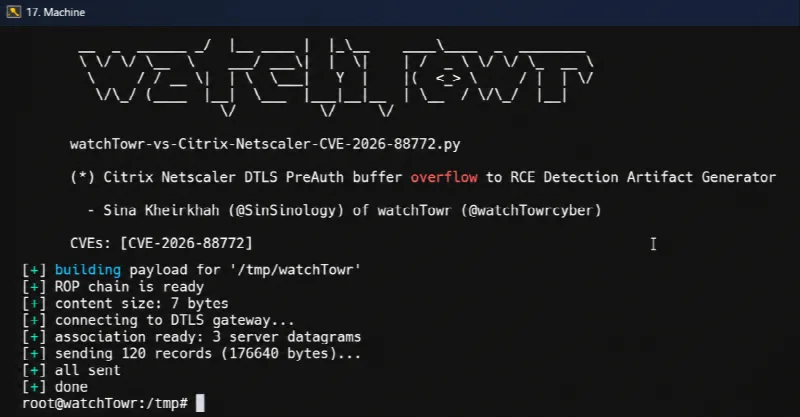
Citrix NetScaler CVE-2026-88772 Exploit Details Show Pre-Auth Path to Shellcode Execution (opens The Hacker News in a new tab)
Cybersecurity researchers have disclosed technical details of a recently patched critical security flaw in Citrix NetScaler ADC and Gateway that has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-88772 (CVSS score: 9.5), has been described as a memory overflow...
-
EU Cyber Resilience Act requirements for containers and Kubernetes (opens Help Net Security in a new tab)
Starting in full force on Dec. 10, 2024, the EU Cyber Resilience Act (CRA) is a regulation (EU 2024/2847) that defines mandatory cybersecurity requirements for all products with digital elements sold in EU markets. Reporting obligations will begin on Sept. 11, 2026, with full enforcement kicking in...
-
In this new SME cybersecurity service, the AI assists and the consultants decide (opens Help Net Security in a new tab)
BH Consulting, the Irish cybersecurity and data protection consultancy, has launched BH Haven, an ongoing service that gives Irish small and medium-sized enterprises (SMEs) access to its specialist consultants, supported by a proprietary AI tool for analysis, evidence review, regulatory mapping and...
-
Most open critical and high flaws are over 90 days old (opens Help Net Security in a new tab)
Detectify analyzed exposure data from 1,293 of its customers in the US, the UK and the Nordics and found that most serious flaws still open on their internet-facing systems are months old. Of the critical and high-severity vulnerabilities open at the time of the snapshot, 97% in the Nordics had...
-
WSL containers are generally available on Windows (opens Help Net Security in a new tab)
Microsoft made WSL containers generally available and shipped the feature with controls that let administrators switch it off or limit where it pulls images from. WSL containers run Linux containers on Windows through the Windows Subsystem for Linux. They install with wsl --update or from...
-
Most organizations need six months or longer to roll out new security controls (opens Help Net Security in a new tab)
Cisco surveyed 8,000 security professionals in 30 markets about how well their organizations defend against AI-era threats, and only 8% landed in the top group. Cisco gave the most weight in its scoring to internal friction, meaning the delays and turf problems inside a company that slow a security...
-
Post-quantum website certificates from Cloudflare are scheduled for early 2027 (opens Help Net Security in a new tab)
Cloudflare plans to become a public certificate authority (CA), an organization that issues the digital certificates websites use to encrypt traffic and prove who they are. The company said that its CA will issue conventional certificates and a post-quantum type called Merkle Tree Certificates...
-
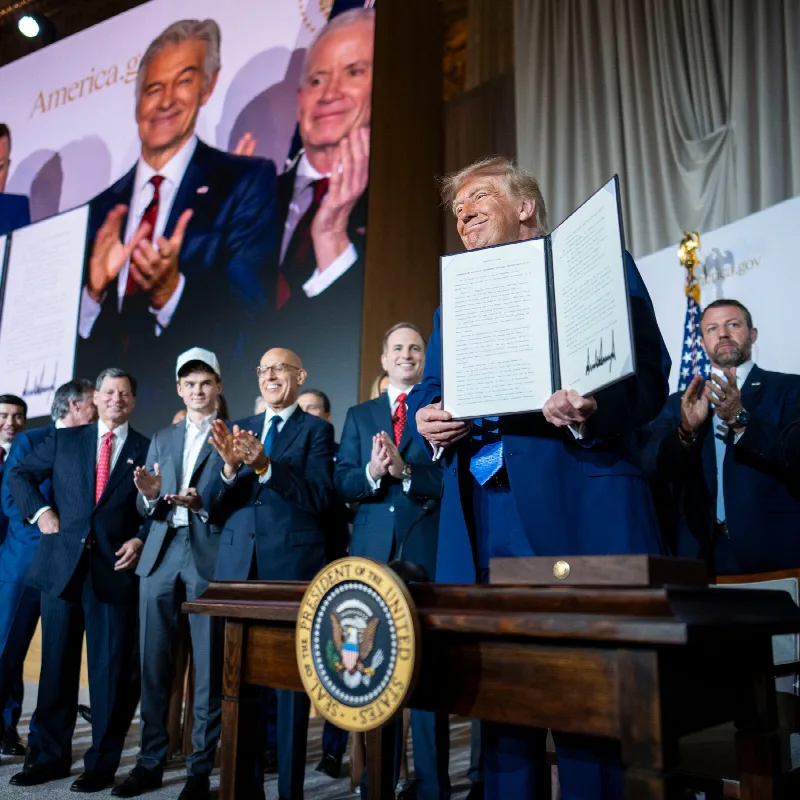
Trump Says Top Tech Firms Have Signed Accord to ‘Self-Police’ AI Development (opens Security Week in a new tab)
The accord opened the door to future regulation but focused on four voluntary steps for the companies to take. The post Trump Says Top Tech Firms Have Signed Accord to ‘Self-Police’ AI Development appeared first on SecurityWeek.
-
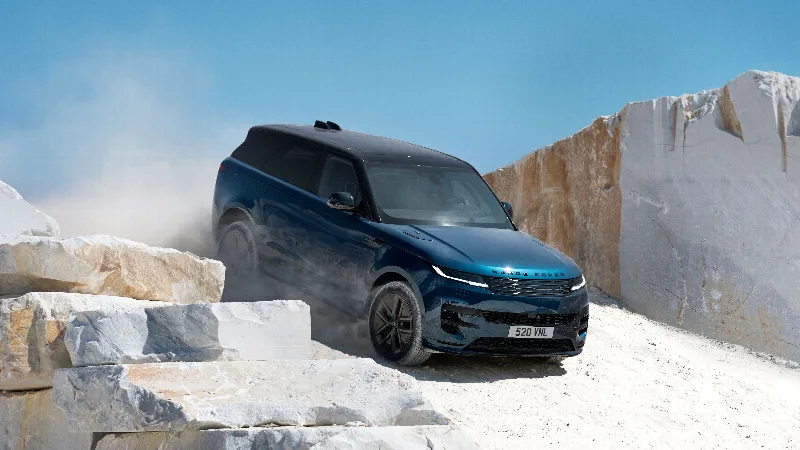
Range Rover Sport Electric: Price, Specs, Availability (opens Wired in a new tab)
By sharing the same platform, the Sport gets the same specs as the classier Range Rover Electric, but with added torque at a smaller outlay.
-
At A.I. Event, Trump Asks Meta, OpenAI and Microsoft to Make Safety Decisions Themselves (opens NY Times in a new tab)
President Trump’s meetings with tech leaders produced some voluntary safeguards and a commitment to rebrand artificial intelligence as “super intelligence,” the term that Mr. Trump prefers.