News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Vulnerability disclosures are rocketing, but AI is changing the types of flaw being discovered (opens IT Pro Security in a new tab)
The number of exploitations has also grown by almost 100%, according to Google
-
Armadin raises $255.5 million to expand AI offensive security platform (opens Help Net Security in a new tab)
Armadin has raised $255.5 million in Series B funding co-led by Andreessen Horowitz (a16z) and Accel that brings the company’s valuation to over $2.5 billion. The round includes participation from new investors Bain Capital Ventures (BCV) and Redpoint. Existing investors 8VC, Ballistic Ventures...
-
Zuckerberg drafted Trump’s AI accord, but Microsoft and Amazon didn’t sign (opens The Next Web in a new tab)
Mark Zuckerberg came up with the AI safety accord that President Donald Trump signed on Tuesday, Semafor and Politico reported. He also circulated the draft. Microsoft and Amazon did not sign it. Satya Nadella and Jeff Bezos both attended the White House lunch where the CEOs agreed it. Ashley Gold...
-
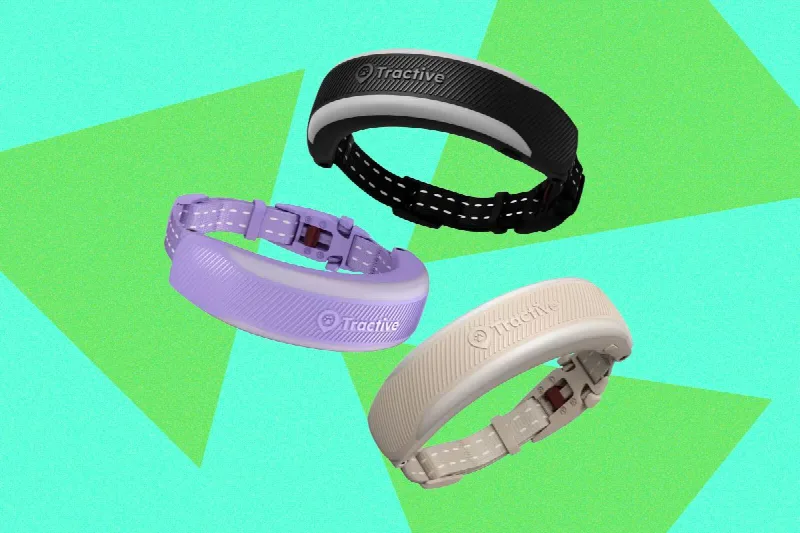
Tractive Cat 6 Mini Review: A Fitbit for Your Cat (opens Wired in a new tab)
Cats are finally getting the dog treatment. This smart cat collar features GPS location, activity, and sleep tracking, plus all-new heart and respiratory rate monitoring.
-
What’s Next for ‘Hard Fork’? (opens NY Times in a new tab)
The podcast’s next chapter begins this week.
-
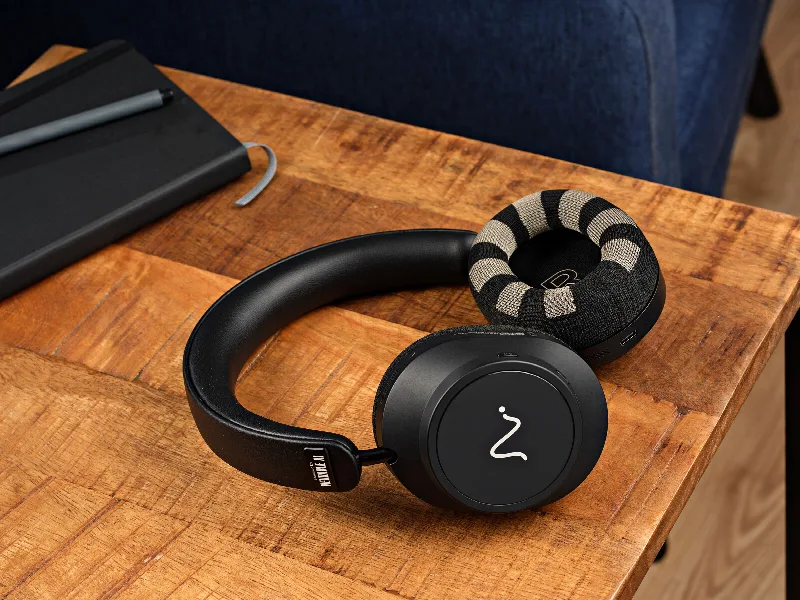
Exclusive: Neurable’s First Brain-Scanning Headphones Want to Fine-Tune Your Focus (opens Wired in a new tab)
The company claims that its new device, the Neurable One, can keep you in the zone, calculate the best time to take a break, and tell you when your “brain battery” needs a recharge.
-
Modernization without disruption: Rethinking the rip-and-replace mindset (opens CIO in a new tab)
I’ve seen organizations reach a point in a modernization program where the technology itself is no longer the biggest risk. A decision was made for a full rip-and-replace. The new environment is ready. The migration plan has been tested. The business case has been approved. But the team responsible...
-
Are forward deployed engineers flirting with failure? (opens CIO Dive in a new tab)
Vendor-led FDE initiatives face cost and efficacy issues that will lead most companies to abandon the model by 2028, according to Gartner.
-
Treasury Blacklists Most-Wanted ATM Malware Developer and His Network (opens Security Week in a new tab)
The US government continues its crackdown on Tren de Aragua over its ATM jackpotting scheme. The post Treasury Blacklists Most-Wanted ATM Malware Developer and His Network appeared first on SecurityWeek.
-
Zammad Zero-Days Exploited in AI-Powered DIVD Hack (opens Security Week in a new tab)
The flaws were chained to hijack sessions, achieve remote code execution, and elevate privileges to root. The post Zammad Zero-Days Exploited in AI-Powered DIVD Hack appeared first on SecurityWeek.
-
OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates (opens The Hacker News in a new tab)
OpenAI on Wednesday said it identified and disrupted a coordinated distillation campaign that was designed to illicitly extract protected reasoning from its artificial intelligence (AI) models. A "core cluster of the activity," going back to the first week of July, has been attributed to...
-
OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates (opens The Hackers News in a new tab)
OpenAI on Wednesday said it identified and disrupted a coordinated distillation campaign that was designed to illicitly extract protected reasoning from its artificial intelligence (AI) models. A "core cluster of the activity," going back to the first week of July, has been attributed to...
-
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504...
-
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV (opens The Hackers News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504...
-
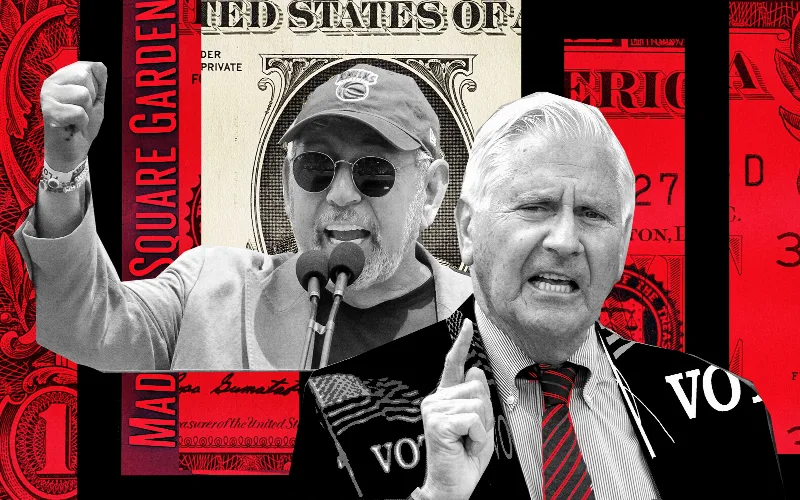
Madison Square Garden’s James Dolan Is Spending Big on New York’s Governor Race (opens Wired in a new tab)
James Dolan has put surveillance at the center of his sports and entertainment empire. Now he’s getting involved in GOP politics by backing a candidate who supports Flock, ICE, and AI data centers.
-
Monk hosts Net 30, an applied AI summit on the future of finance (opens The Next Web in a new tab)
On October 21, 150 CFOs, operators, founders and researchers will gather at The Times Center in New York. They will discuss how AI is reshaping cash, capital and the finance function. In a Gartner survey of 183 CFOs, 84% of finance organizations had deployed AI or planned to. Yet only 7% reported a...
-
Suspected Chinese hackers posed as US AI insiders, Proofpoint says (opens The Next Web in a new tab)
A group of hackers believed to have been acting on behalf of China pretended to be well-known American AI experts to obtain the email accounts of people who specialize in AI policy. According to Reuters, the security firm Proofpoint released the findings on Thursday. Proofpoint has identified the...
-
New Cisco SD-WAN zero-day exploited in-the-wild (CVE-2026-76504) (opens Help Net Security in a new tab)
For the fifth time this year, Cisco revealed attackers have exploited a vulnerability (CVE-2026-76504) in its SD-WAN solution in zero-day attacks. The vendor’s incident responders became aware of active exploitation of this vulnerability in September 2026, after getting pinged and resolving a Cisco...
-
UK schools are getting better at dealing with cyber attacks (opens IT Pro in a new tab)
Most now say they can recover immediately, and that they're taking proactive measures to protect themselves
-
UK schools are getting better at dealing with cyber attacks (opens IT Pro Security in a new tab)
Most now say they can recover immediately, and that they're taking proactive measures to protect themselves