News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
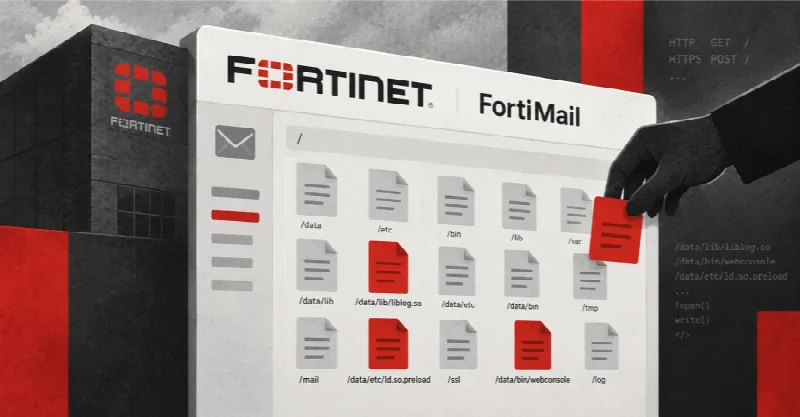
Critical FortiMail zero-day exploited in the wild (CVE-2026-104286) (opens Help Net Security in a new tab)
Fortinet is warning customers that attackers are exploiting a zero-day vulnerability (CVE-2026-104286) in FortiMail, its email security gateway. Fortinet says the flaw has been reported to be exploited in the wild, and urges customers to apply the workaround it shared until fixes are available...
-
AI broke the economics of software. Vayu wants to be the first to tell a CFO which customers are losing them money (opens The Next Web in a new tab)
Here is a problem the software industry did not have three years ago. A customer signs a contract for an AI product. They use it heavily, which is what every vendor wants. Every one of those uses costs the vendor money: tokens, compute, third-party model calls. The invoice goes out at the agreed...
-
AI Agents Aimed SQL Injection at US and Canadian Government Sites (opens Security Week in a new tab)
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI. The post AI Agents Aimed SQL Injection at US and Canadian Government Sites appeared first on SecurityWeek.
-
French state-owned Bull doubles supercomputer output at Angers factory (opens The Next Web in a new tab)
Bull, the French state-owned supercomputer maker, has doubled production at its factory in Angers, western France, after an €80 million rebuild. The plant now assembles 12 racks a month, up from six, executives told Reuters, which first reported the expansion on Thursday. Output could rise to 24...
-
EU Cyber Resilience Act ‘completely kills’ manual vulnerability triage (opens CSO Online in a new tab)
Independent security experts see the EU Cyber Resilience Act (CRA) reshaping international technology markets to emphasize cyber resilience from the ground up, thereby testing the operational capacities of technology vendors whose wares compete in those markets. The EU CRA introduces mandatory...
-
Two Zero-Days Exploited in Attack on Dutch Institute for Vulnerability Disclosure (opens Infosecurity Magazine in a new tab)
The Dutch Institute for Vulnerability Disclosure reveals agentic AI-powered attack using Zammad zero-days
-
SoftBank completes $30bn OpenAI investment with final $10bn payment (opens The Next Web in a new tab)
SoftBank Group has completed its $30bn follow-on investment in OpenAI, after paying the third and final $10bn tranche on 1 October, Japan time. The Japanese group made the payment through its Vision Fund 2, it said on Thursday. With this payment, SoftBank has now put $64.6bn into OpenAI in total...
-
NetApp Insight 2026: Can Novus and Keystone break the AI bottlenecks? (opens IT Pro Cloud in a new tab)
We're back in Vegas as Ross Kelly talks us through all the news from NetApp Insight 2026
-
Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action (opens Security Week in a new tab)
CVE-2026-104286 is a critical-severity path traversal vulnerability that could allow attackers to write arbitrary files to the system. The post Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action appeared first on SecurityWeek.
-
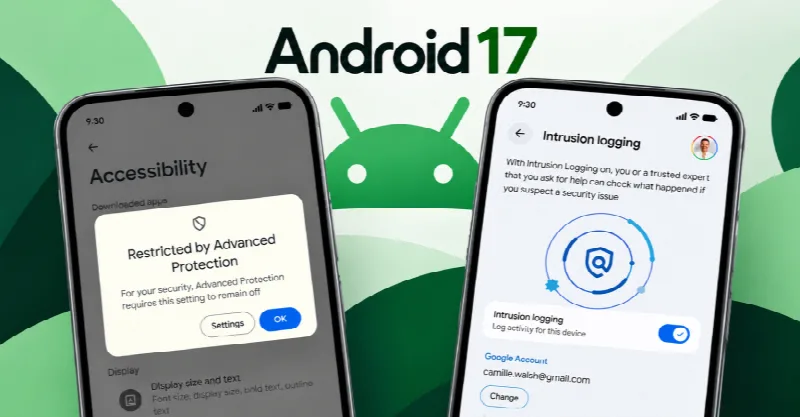
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools (opens The Hacker News in a new tab)
Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and...
-
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools (opens The Hackers News in a new tab)
Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and...
-
AI could boost software engineer productivity by 32.6% (opens CIO in a new tab)
Tools such as Anthropic Claude Code or OpenAI Codex have changed the face of software development, and all the signs are that this investment is set to increase further. But is paying a monthly subscription (and perhaps additional usage fees) cost-effective? Will the increasing level of investment...
-
Criminal recruiters want people on your payroll (opens Help Net Security in a new tab)
Legitimate employee access can let criminals circumvent security controls that would be difficult to overcome from outside an organization. Routine actions such as information lookups, account resets, transaction approvals and shipment changes can become services sold to criminal customers...
-
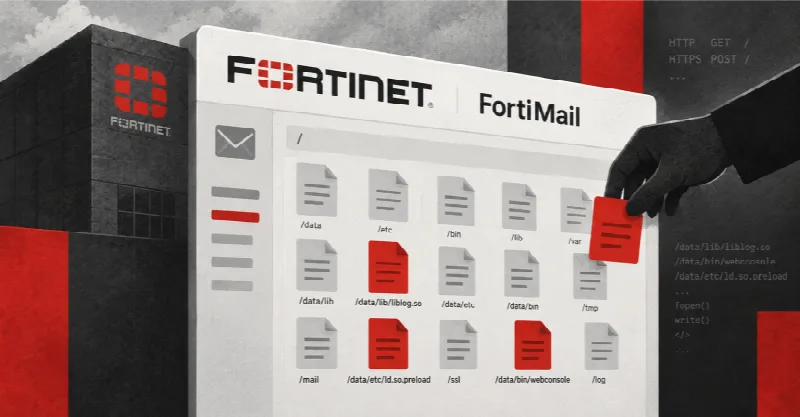
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8)...
-
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes (opens The Hackers News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8)...
-
Android 17 makes it harder for spyware to cover its tracks (opens Help Net Security in a new tab)
When a journalist suspects their phone has been hacked, the first question is whether any trace of the attack is left. Google has added six features to Advanced Protection in Android 17, including one that keeps a copy of that evidence off the device. Existing users will receive a notification when...
-
Botnets, adversarial attacks and data poisoning top leaders’ AI threat list (opens Help Net Security in a new tab)
Companies are putting more money into AI while naming attacks on AI systems as the threat they are least ready to face. PwC surveyed 3,934 business and technology leaders in 71 countries between May and July 2026. Half of the security and technology executives among them ranked such attacks in...
-
AI agents keep access to company data after their work is done (opens Help Net Security in a new tab)
IT teams responsible for identity security are concerned about AI agents’ ongoing access to company systems and the actions they take on users’ behalf, according to a Delinea’s 2026 Identity Security Report: The AI Enforcement Gap. “Written policy is only as good as your ability to enforce it at...
-
New infosec products of the week: October 2, 2026 (opens Help Net Security in a new tab)
Here’s a look at the most interesting products from the past week, featuring releases from BlackFog, Genea, Vega, and Thales. Vega II brings security-trained AI and lasting memory to the SOC Vega has introduced Vega II, its biggest platform release since emerging from stealth. The update brings...
-
Omnissa delivers a peek into the benefits of breaking through enterprise data silos (opens CIO in a new tab)
When Omnissa this week rolled out a new AI governance authority product, Elara, in beta, it delivered a glimpse into the potential of having visibility between the typical enterprise’s data silos, whether they’re in lines of business, disparate geographies, or corporate operational units. “By...