News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
The executive playbook for scaling AI: Start with data modernization (opens CIO Dive in a new tab)
AI success starts with trusted data. Learn how modernization accelerates AI at scale.
-
Work is evolving, are your environments designed to keep up? (opens CIO Dive in a new tab)
Learn how a platform approach can help create more scalable, adaptable workplaces.
-
Sam Altman tells Politico the world “should accept some harm from AI” (opens The Next Web in a new tab)
OpenAI chief Sam Altman says the gains from AI are worth some harm. He also says the tech should stay open to the public. Altman made the comments in an interview with Politico for the first edition of Decoded. The new daily tech newsletter and podcast launches on Monday. TNW has not seen the full...
-
Should the CISO role be split in two? (opens CSO Online in a new tab)
In its roughly 30-year history, the CISO role has been reshaped by waves of new technology and rising cyber threats. In many organizations, CISOs now own risk reporting, information risk management, threat monitoring, cyber risk accountability and governance, and security strategy. And as AI and...
-
Should the CISO role be split in two? (opens CSO Online in a new tab)
In its roughly 30-year history, the CISO role has been reshaped by waves of new technology and rising cyber threats. In many organizations, CISOs now own risk reporting, information risk management, threat monitoring, cyber risk accountability and governance, and security strategy. And as AI and...
-
Apple tightens macOS disk access as AI agents become more powerful (opens Help Net Security in a new tab)
Apple plans to introduce additional controls for Full Disk Access in macOS, citing growing privacy risks as AI agents become more capable and autonomous. Users will need to take explicit action to grant apps this permission. The company has not specified a rollout date or detailed how the controls...
-
Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE (opens The Hacker News in a new tab)
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of session forgery stemming from the use of a weak pseudo-random number generator (PRNG)...
-
Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE (opens The Hackers News in a new tab)
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of session forgery stemming from the use of a weak pseudo-random number generator (PRNG)...
-
doxx.net opens Agentic Defined Networking public beta, raises $38 million (opens Help Net Security in a new tab)
doxx.net has launched the open beta of its Agentic Defined Networking (ADN) platform, which lets people and their agents create their own private, secure networks, communicate with no servers in the middle, and get started with no personal information required. The platform gives agents an...
-
Elon Musk says SpaceXAI will be renamed SpaceXSI after Trump’s AI order (opens The Next Web in a new tab)
Elon Musk said on Sunday that SpaceX’s artificial intelligence unit, SpaceXAI, will change its name to SpaceXSI. The plan follows an order from US President Donald Trump directing federal agencies to drop the term “artificial intelligence.” Musk confirmed the change in a reply on X, Reuters...
-
AI slop submissions force Google to freeze its open-source bug bounty (opens Help Net Security in a new tab)
Google has stopped accepting new product vulnerability reports through its Open Source Software Vulnerability Reward Program (OSS VRP), after a wave of invalid, AI-generated submissions swamped the engineers and open source maintainers who review them. The rules page for Google’s OSS VRP states...
-
Alleged ShinyHunters Leader Arrested in Jordan (opens Security Week in a new tab)
Known as Rey, the suspect is reportedly helping the FBI identify and locate other members of the extortion group. The post Alleged ShinyHunters Leader Arrested in Jordan appeared first on SecurityWeek.
-
New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline (opens The Hacker News in a new tab)
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and Citrix NetScaler Gateway that has been exploited as part of targeted zero-day attacks. The vulnerability, tracked as CVE-2026-88779, carries a CVSS score of 8.7 out of 10.0. "CVE-2026-88779 is a memory...
-
New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline (opens The Hackers News in a new tab)
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and NetScaler Gateway that has been exploited as part of targeted zero-day attacks. The vulnerability, tracked as CVE-2026-88779, carries a CVSS score of 8.7 out of 10.0. "CVE-2026-88779 is a memory overflow...
-
Exclusive: Danish legal research startup Pandektes raises €13.5M Series A (opens The Next Web in a new tab)
Building a company like this requires relentlessness, belief and dedication. Every start-up will have low points, but we’ve always as founders had this die hard conviction that we could build a better and new way to do legal research, said Casper Laursen, CEO and co-founder of Pandektes. The law is...
-
Three questions a hospital CISO should ask a healthcare fintech vendor (opens Help Net Security in a new tab)
In this Help Net Security interview, Drew McCombs, CTO and CISO at Cylerity, explains how he balances both roles. Security work is scheduled into every sprint, and issues touching patient data or funds disbursement come first. He covers how Cylerity keeps PHI away from its bank partner, why AI...
-
Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier (opens Security Week in a new tab)
Citrix has confirmed that a new zero-day vulnerability, CVE-2026-88779, emerged just days after two other exploited flaws were patched. The post Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier appeared first on SecurityWeek.
-
Keyorix: Open-source secrets management for teams that can’t use SaaS (opens Help Net Security in a new tab)
Keyorix is an open-source secrets manager that runs entirely on a company’s own servers. A secrets manager is the locked store where an application fetches the database passwords, API keys, and tokens it needs, so they stay out of config files and source code. It ships as one binary and, in its...
-
How RMM abuse gives attackers a way in that looks like business as usual (opens Help Net Security in a new tab)
Huntress found attackers using legitimate remote monitoring and management (RMM) software in 45% of the endpoint-related incidents it recorded in the first quarter of 2026. The security company also ranked 11 attack tactics by how often it sees them and how much damage each can do, and RMM abuse...
-
Court Tosses Sentence After A.I. Video of Victim ‘Forgiving’ His Killer Is Played (opens NY Times in a new tab)
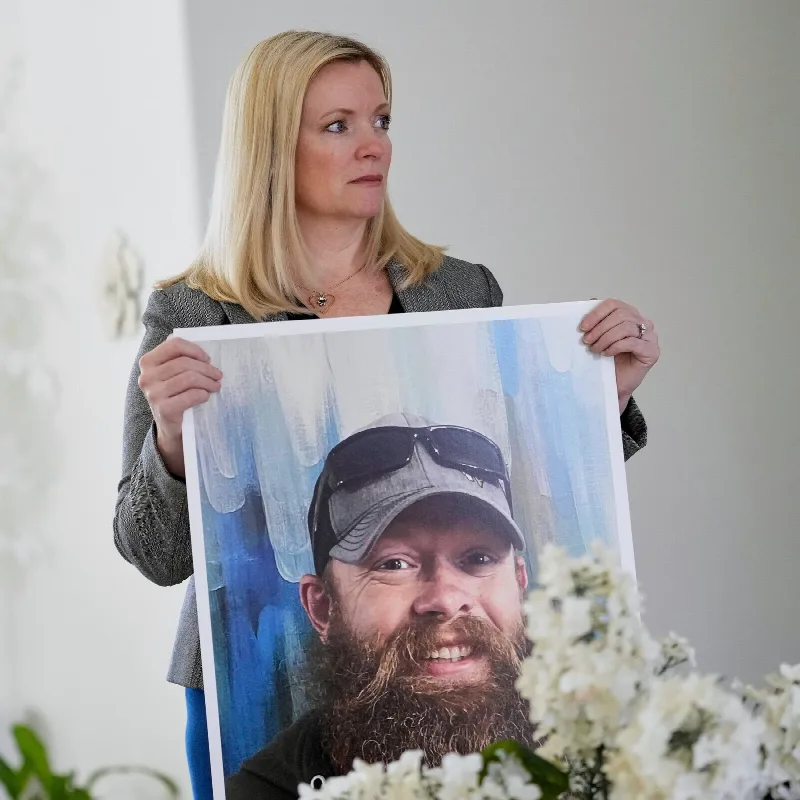
An appellate court in Arizona threw out the prison sentence of a man convicted of manslaughter after an A.I.-generated video of his victim was played in court.