News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Zendesk CEO Tom Eggemeier says Meta’s Muse saved him $3,105 in five days (opens The Next Web in a new tab)
Zendesk will end the year with about $400m of AI revenue, up from about zero two years ago, chief executive Tom Eggemeier told TNW. Most of it comes from AI agents that customers pay for only when they resolve a case. Eggemeier has run Zendesk since late 2022. Before that, he was a partner at […]...
-
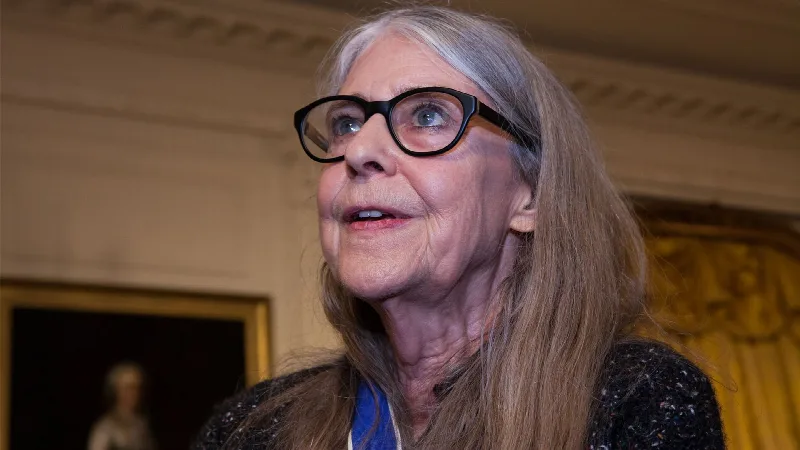
Software engineering trailblazer Margaret Hamilton dies aged 90 (opens IT Pro in a new tab)
Hamilton played a key role in the Apollo 11 program and early software engineering
-
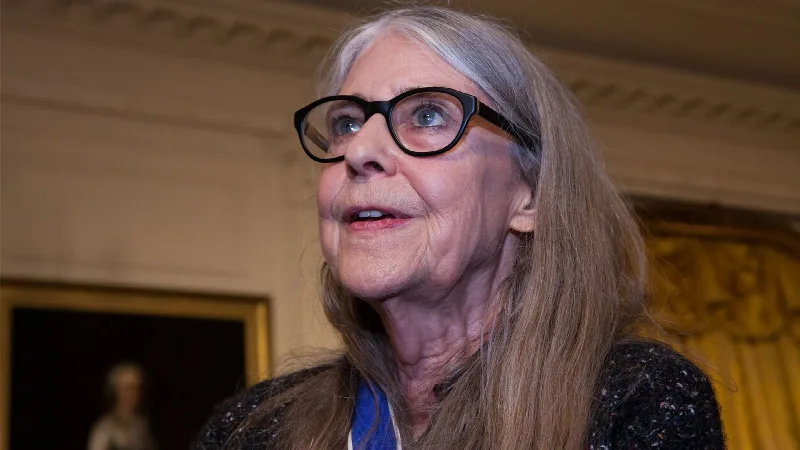
Software engineering trailblazer Margaret Hamilton dies aged 90 (opens IT Pro Security in a new tab)
Hamilton played a key role in the Apollo 11 program and early software engineering
-
Oracle Health Data Breach Tally Climbs to Nearly 20 Million (opens Security Week in a new tab)
The figure is far higher than the counts that surfaced in earlier filings and patient notifications. The post Oracle Health Data Breach Tally Climbs to Nearly 20 Million appeared first on SecurityWeek.
-
UK defence firms plan to invest £19.75bn over the next year (opens The Next Web in a new tab)
UK defence companies plan to invest a combined £19.75bn over the next 12 months, according to new research from law firm White & Case. Research company Censuswide surveyed 250 senior decision-makers at UK defence companies and defence technology start-ups for the study between 17 and 24 September...
-
Ransomware recovery firm boss charged with secretly paying attackers and overcharging victims (opens Help Net Security in a new tab)
The owner of Florida-based ransomware remediation company MonsterCloud has been charged with fraud for allegedly paying ransomware gangs behind his clients’ backs and billing them far more than the ransom. Zohar Pinhasi (aka “Zack Silver” and “Zack Green”), a 50-year-old US and Israeli national...
-
FortiBleed Attackers Locking Victims Out of Fortinet Devices (opens Security Week in a new tab)
Attackers are creating new accounts and deleting existing ones and passwords to prevent legitimate access. The post FortiBleed Attackers Locking Victims Out of Fortinet Devices appeared first on SecurityWeek.
-
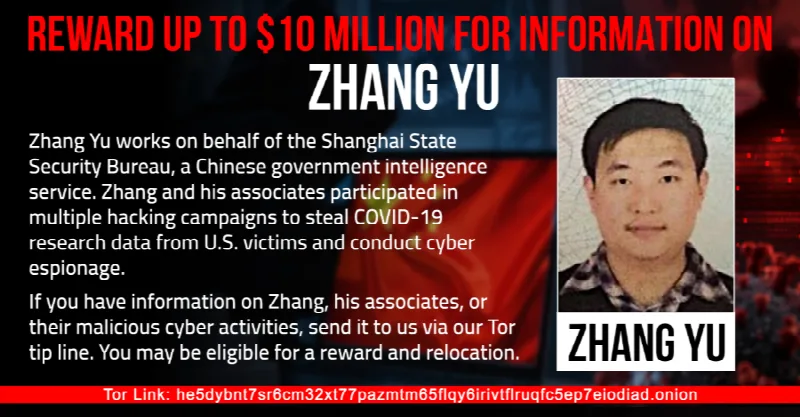
U.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM Hacks (opens The Hacker News in a new tab)
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM. The reward is for information leading to his...
-
MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data (opens The Hacker News in a new tab)
The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data. Zohar Pinhasi (aka...
-
Adobe will power Heathrow’s new website and AI search push (opens The Next Web in a new tab)
Heathrow Airport has extended its partnership with Adobe and will rebuild its main website on Adobe’s AI customer experience software, the two companies announced on 8 October. The new site will run on Adobe CX Enterprise. The system uses AI agents, software that can carry out tasks on its own, to...
-
Pricing your bad days and how to build an economic model for security decisions (opens Help Net Security in a new tab)
Ivan Milenkovic, VP Risk Technology EMEA at Qualys, explains how security leaders can build an economic model that puts money behind their decisions. He suggests starting with a few loss scenarios, then working down to the assets that drive them. He covers how to rank fixes by value at risk, what...
-
Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm (opens The Hacker News in a new tab)
The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The malicious version 0.5.144 "contains obfuscated malware that harvests...
-
Who watches the AI watching your street? (opens Help Net Security in a new tab)
Yusaku Fujii, a professor at Gunma University in Japan, has designed audits and penalties to stop operators from misusing AI that analyzes street camera footage. His system adds an independent record-keeper and unannounced spot checks to the AI’s outputs. Fujii’s test setting is what he calls a...
-
How AI can fix cybersecurity compliance: From dashboards to continuous execution (opens Help Net Security in a new tab)
Most compliance work goes into proving security, not improving it. That isn’t because the rules are unreasonable. Regulators, customers, and cyber insurers are right to expect organizations to implement hundreds of technical and administrative controls, monitor their environments, respond to...
-
The people who know passkeys best are still typing passwords (opens Help Net Security in a new tab)
Yubico and Okta asked 1,890 technology and security professionals across nine countries how they sign in to work accounts. The most common answer was a username and password, at 43%, from a group in which 87% said they were familiar with passkeys. High familiarity with modern authentication...
-
Java library vulnerabilities: IBM and Red Hat fix 400+ previously unknown flaws (opens Help Net Security in a new tab)
IBM and Red Hat have found and fixed more than 400 previously unknown vulnerabilities in widely used Java libraries through Lightwell, their program for patching open source code that companies already run in production. Companies running the affected libraries are exposed until they apply the...
-
IBM and Red Hat report hundreds of open source fixes with Lightwell Clearinghouse scheme (opens IT Pro in a new tab)
Lightwell Clearinghouse is now generally available, allowing firms to request priority review and remediations for open source software
-
SonicWall’s latest critical flaw indicates a security pattern, not another one-off bug (opens CSO Online in a new tab)
SonicWall has disclosed yet another critical flaw in one of its core products. CVE-2026-102255, rated 10 in severity, the highest possible on the Common Vulnerability Scoring System (CVSS), is a pre-authentication server-side request forgery (SSRF) vulnerability in the SMA1000 Appliance Work Place...
-
New Google Gemini setting could give AI tool broad access to users' Macs (opens IT Pro in a new tab)
A new permission would allow an AI agent to access files and carry out actions without specific permission every time
-
A.I. Music Fraudster Who Drew Millions in Royalties Is Sentenced to 18 Months (opens NY Times in a new tab)
Prosecutors say Michael Smith flooded music-streaming platforms with bots that repeatedly streamed his A.I.-generated music, earning him as much as $8 million.