News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
L’Italia è afflitta da vulnerabilità informatiche, senza una causa chiara (opens Dark Reading in a new tab)
I ricercatori non riescono a spiegare del tutto perché le minacce informatiche in Italia siano così diverse rispetto a quelle di qualsiasi altro Paese.
-
TeamViewer Flaw Lets Remote Computers Attack Users Who Connect to Control Them (opens The Hacker News in a new tab)
TeamViewer has fixed a flaw that lets the machine being controlled in a remote session attack the computer that connected to control it. In a TeamViewer session, the computer that connects and takes control is the viewer, and the machine it controls is the host. A malicious or compromised host can...
-
Binance Suspends Withdrawals After Crypto Hackers Steal $6.3 Billion (opens NY Times in a new tab)
The crypto exchange said it was compromised in what could be the biggest crypto heist ever. One research lab attributed the theft to “North Korea’s elite hacking unit.”
-
PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress (opens Security Week in a new tab)
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week. The post PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress appeared first on SecurityWeek.
-
Stearns and Foster Promo Codes: $300 Off in November 2026 (opens Wired in a new tab)
Discover the best Stearns and Foster promo codes, discounts, and deals to elevate your sleep experience with premium comfort and quality.
-
I Spent 30 Minutes With Apple’s CEO. Now I Know Why John Ternus Got the Job (opens Wired in a new tab)
Apple doesn’t need fixing, and it doesn’t want drama. Its new leader is a “product guy” who bleeds six colors.
-
Lakeside Software taps Mark Benson to lead EMEA channel strategy (opens IT Pro in a new tab)
The appointment comes as the digital employee experience (DEX) vendor looks to expand its partner ecosystem around the SysTrack platform
-
In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak (opens Security Week in a new tab)
Noteworthy stories that might have slipped under the radar: Iran eyed in military freezer hacks, Copenhagen University breach, AI-powered malware. The post In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak appeared first on SecurityWeek.
-
Undead Software Projects Continue to Raise Security Risks (opens Dark Reading in a new tab)
A security firm patched a decade-old app to prevent the takeover of millions of machines, highlighting that abandoned domains remain a boon to attackers.
-
WordPress RCE Flaw Draws Nearly 63,000 Attack Attempts in Just 24 Hours (opens The Hacker News in a new tab)
Threat actors have been observed attempting to exploit a high-severity security flaw in WordPress Core shortly after patches were released. The vulnerability, which does not have a CVE identifier, relates to a case of remote code execution impacting WordPress Core versions 4.7 through 7.1.3. It...
-
Big Tech’s Data Center Blitz Is Burning Through Cash and Scaring Wall St. (opens NY Times in a new tab)
Amazon became the latest tech company to announce swelling investments in A.I. amid stumbling share prices.
-
Passkeys Are Better Than Passwords. But They Are Not Enough. (opens Security Week in a new tab)
As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it. The post Passkeys Are Better Than Passwords. But They Are Not Enough. appeared first on SecurityWeek.
-
Bulletproof Host Virtualine Loses Its Domain to FBI Seizure (opens Security Week in a new tab)
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments. The post Bulletproof Host Virtualine Loses Its Domain to FBI Seizure appeared first on SecurityWeek.
-
Assad regime hacker who caused $136 billion market drop sentenced to 42 months (opens Help Net Security in a new tab)
A Syrian man who used a hijacked news agency Twitter account to post a fake report of explosions at the White House has been sentenced to 42 months in prison, the US Department of Justice has announced. Ahmad Umar Agha, also known as “Th3Pr0”, was sentenced on Thursday by a federal court in the...
-
Shufti ties AI agent actions to verified owners and permissions (opens Help Net Security in a new tab)
Shufti launches Know Your Agent (KYA), an AI agent verification solution designed to verify autonomous AI agents acting on behalf of individuals and businesses. Agentic commerce enables AI agents to open accounts, place orders, and move funds for their owners. A business receiving one of these...
-
Bedrock Data routes data exposure fixes to owners and verifies results (opens Help Net Security in a new tab)
Bedrock Data has announced AI-assisted remediation, which federates the work of fixing data exposure to the data owners across the enterprise. Bedrock Data discovers who owns each exposed dataset, opens a ticket for that owner in the Jira or ServiceNow workflow the enterprise already runs and...
-
Anthropic AI model finds Linux kernel bug that leads to remote root access (opens CSO Online in a new tab)
Linux servers running Multipath TCP (MPTCP) could be vulnerable to remote code execution through a flaw in the kernel’s networking stack. Anthropic has disclosed a zero-click exploit developed with an unreleased Claude research model that allows an unauthenticated attacker to execute arbitrary...
-
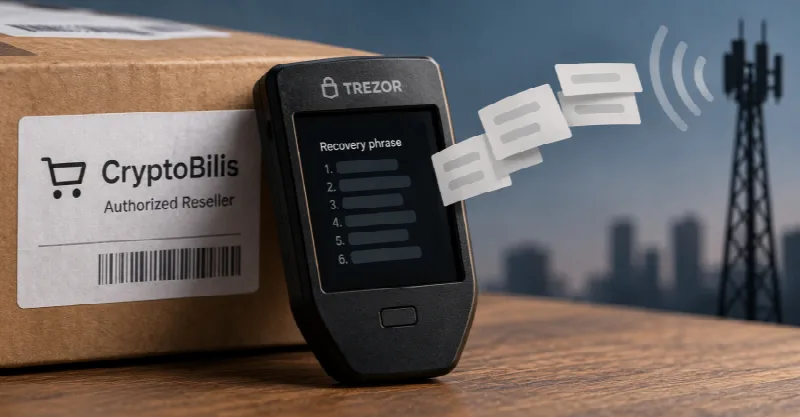
Trezor Warns of Suspected Hardware Implant in One of Its Wallets Sold by CryptoBilis (opens The Hacker News in a new tab)
A Trezor Safe 5 hardware wallet bought from the reseller CryptoBilis has an extra circuit board that sends out the recovery phrase over a mobile network, a customer has reported. Trezor has not yet examined the device. It is telling everyone who bought a Trezor from CryptoBilis since March 2026 to...
-
Fresh WordPress Vulnerability in Attackers’ Crosshairs (opens Security Week in a new tab)
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution. The post Fresh WordPress Vulnerability in Attackers’ Crosshairs appeared first on SecurityWeek.
-
Chinese Actor Compromises US Government Network Via Chained PHP2Shell Exploit (opens Infosecurity Magazine in a new tab)
Dream found that a suspected Chinese-nexus actor gained root access to Palo Alto Network firewall servers to target government organizations